
Responsive Banner Design

What is brute force attack?

Brute force attacks

Attackers systematically try large numbers of passwords, encryption keys or login credentials until one works, gaining unauthorized access to your systems.

Why it works

Slow and resource-heavy, but often effective against weak passwords and poorly configured systems.

Common variants

Dictionary attacks use common passwords, while credential stuffing replays leaked ones across many accounts. Strong security practices are essential to defend against them.

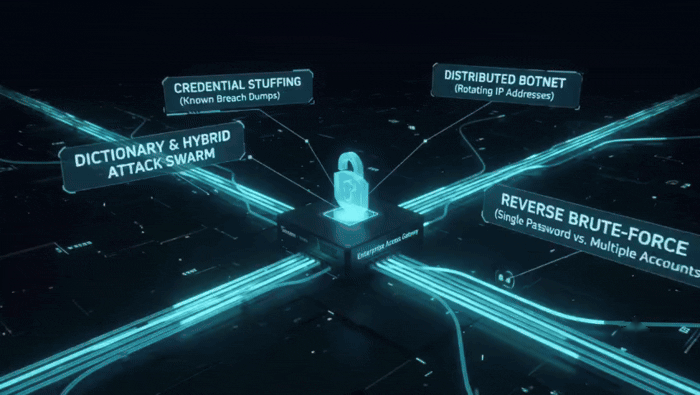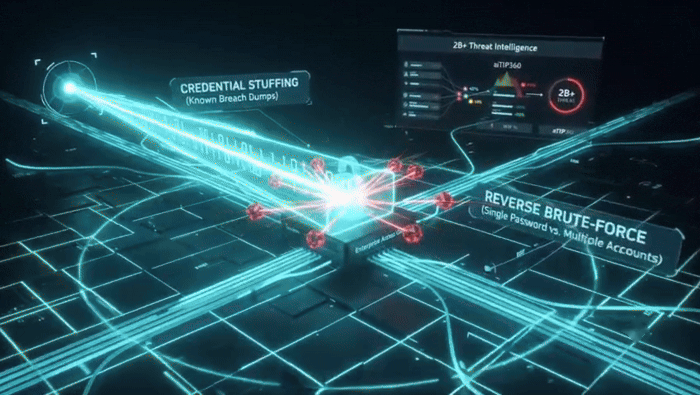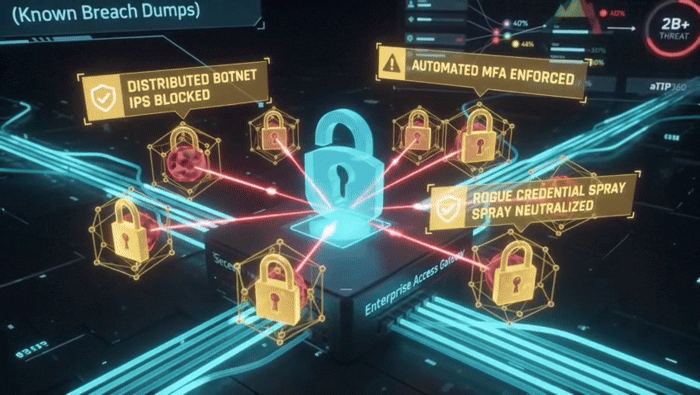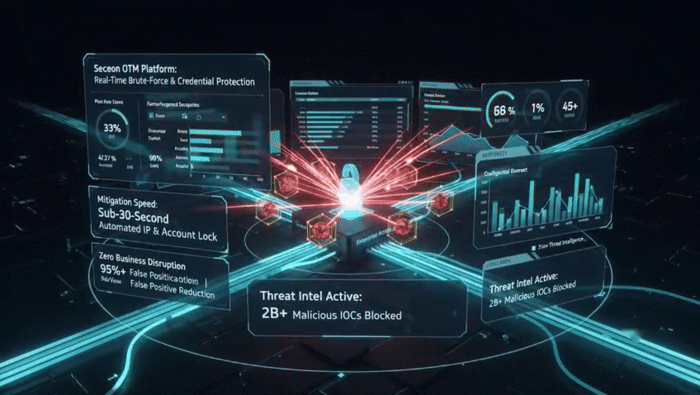
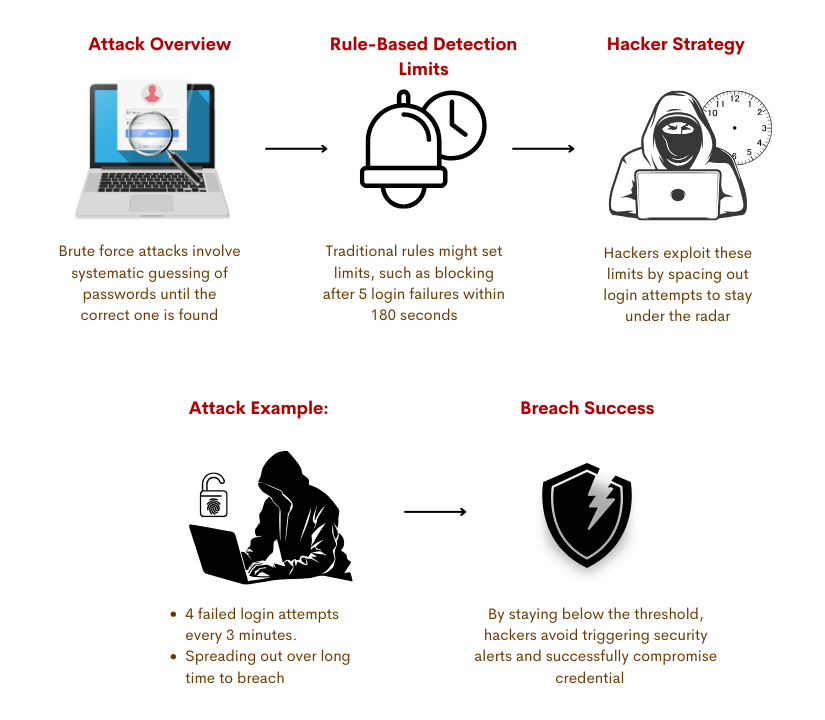
How a low-and-slow brute force attack stays under rule-based login limits
Seceon OTM Platform

Stop brute force attacks before an account falls

Detect password guessing, spraying and credential stuffing across every login surface, then contain the attacker automatically.

Built-in detections

Brute force alerts, out of the box

Detections run on streaming telemetry in near real time, and on historical data for retrospective analysis.

Example rule: 10 or more failed logins for multiple usernames from the same source IP within 5 minutes raises a High-severity password spraying alert.

UEBA

Behavioral baselines

Flags unusual login failures and impossible travel against each user's normal pattern.

Threat intelligence

Known-bad sources

2B+

IOCs from 100+ sources, re-matched against history when new intelligence arrives

aiSecurity UIDGuard360

Cross-platform view

Aggregates failed logins across identity platforms to catch distributed attacks.

OktaAzure ADAWSSaaS

MITRE ATT&CK

Mapped coverage

Includes MFA fatigue bombing detection.

T1110T1110.001T1110.003T1621

Correlation

Failures followed by a success

Repeated failed logins followed by a successful one, especially from an unusual location, raise a compromised-credentials alert.

Example: login attempts on one account

✕ Failed✕ Failed✕ Failed✕ Failed → ✓ Success
↓ Compromised credentials alert

Automated response

<90s

Containment

With rollback if a false positive is confirmed.

70%+

SERA AI

Autonomous L1 investigation

Investigates routine alerts, explains the root cause and escalates only confirmed threats.

45+

aiCompliance CMX360

Audit-ready reporting

Compliance frameworks supported, with every detection and response action logged in an immutable audit trail.

Types Of Brute Force Attack

Each brute force attack might utilize a variety of tactics to unearth confidential information. Any of the following common brute force techniques could be used against the intended victim:

Evolve Section

Crypto Ransomware IconSimple Brute Force Attack

Trying all possible passwords without any specific logic.

Locker Ransomware IconDictionary Attack

Using a pre-defined list of common passwords (like "password123" or "qwerty") to guess the correct one.

Double Extortion IconCredential Stuffing

Using lists of known username-password combinations (often from previous data breaches) to gain unauthorized access.

Hybrid Attack IconHybrid Attack

Combining a dictionary attack with brute force by slightly altering known words (e.g., "password1," "password2").

Hybrid Attack IconReverse Brute Force Attack

Targets a single password against multiple accounts, seeking to compromise as many as possible

Hybrid Attack IconDistributed Brute Force Attack

Uses multiple systems to simultaneously guess passwords, overwhelming defenses and increasing attack speed.

Key Challenges

Ransomware attacks present several significant challenges
Password Complexity

 Lack of security hygiene, particularly for password creation and maintenance, making it easier for attackers to succeed.

Encryption and Hashing

Poorly implemented encryption or weak hashing algorithms can make brute force attacks easier.

Account Lockout Policies

 Implementing policies that lock accounts after a certain number of failed attempts can mitigate brute force attacks but may lead to denial-of-service (DoS) scenarios if not handled carefully.

Offline attacks

 Where attackers gain unauthorized access to a system and perform actions without the need for ongoing network connectivity, are often more effective and harder to detect.

Computational Power

 Modern computing power, especially with the advent of GPUs and cloud computing, has made brute force attacks more feasible.

IP Address Rotation

 Attackers often use IP address rotation or distributed networks (e.g., botnets) to bypass IP-based rate-limiting, making brute force attacks harder to block and detect.

Summary Section

Summary

Seceon’s AI-driven solution detects and prevents brute force attacks by monitoring anomalous access patterns, automatically blocking threats in real-time to ensure strong protection and maintain system integrity against unauthorized access attempts.

Brute Force Prevention FAQs

Learn how to detect brute force attacks, identify suspicious authentication patterns, protect enterprise accounts, and strengthen threat detection with Seceon.

How can organizations detect brute force attacks before attackers gain unauthorized access?

Organizations can detect brute force attacks by monitoring login activity, failed authentication attempts, unusual access patterns, and repeated attempts against individual or multiple accounts. Behavioral analytics and security event correlation help identify suspicious activity that may indicate automated password guessing or credential abuse.

Seceon's OTM Platform uses AI/ML-driven analytics to monitor security events and identify patterns associated with brute force attacks. This helps security teams investigate suspicious login activity and take appropriate action before an attack escalates.

How can AI detect distributed brute force attacks that bypass traditional security rules?

AI-driven detection can help identify distributed brute force attacks by correlating authentication events across multiple IP addresses, accounts, devices, and systems. Unlike detection methods that rely only on a fixed threshold for failed logins, behavioral analytics can identify unusual patterns across related events.

Seceon's OTM Platform analyzes security events using AI/ML-driven analytics and event correlation to help identify suspicious login behavior, including patterns that may be missed when events are investigated individually.

What is the best way to prevent password spraying and credential stuffing attacks in enterprise environments?

Preventing password spraying and credential stuffing requires multiple layers of defense, including multi-factor authentication (MFA), strong and unique passwords, login rate limiting, suspicious-IP controls, and continuous authentication monitoring. Organizations should also monitor attempts involving known compromised credentials and repeated login failures across multiple accounts.

Seceon's OTM Platform helps security teams detect suspicious authentication patterns through security monitoring, behavioral analytics, and threat intelligence. When integrated with appropriate security controls, these capabilities can support timely investigation and response to credential-based attacks.

How can security teams detect brute force attacks when attackers rotate IP addresses or use botnets?

Security teams can detect brute force attacks involving rotating IP addresses or botnets by correlating login attempts across multiple sources instead of relying exclusively on blocking individual IP addresses. Useful indicators include repeated authentication failures, unusual access locations, attempts against multiple accounts, and abnormal login activity over time.

Seceon's OTM Platform provides centralized security visibility and uses AI/ML-driven analytics and threat intelligence to help identify suspicious activity across supported data sources. Correlating these events can help security teams recognize distributed attack patterns and investigate potential account compromise.

Which cybersecurity platforms can automatically detect and respond to brute force attacks in real time?

Cybersecurity platforms designed for automated threat detection and response can monitor authentication events, correlate suspicious activity, enrich alerts with threat intelligence, and initiate configured response actions. Organizations should evaluate supported integrations, response playbooks, account-protection controls, and approval requirements before deployment.

Seceon's OTM Platform combines SIEM, XDR, SOAR, and threat intelligence capabilities to support threat detection and response workflows. Depending on available integrations and configuration, response actions may include blocking suspicious IP addresses, locking targeted accounts, and triggering additional authentication controls.

How can MSSPs manage brute force attack detection and prevention across multiple customers?

MSSPs can manage brute force detection across multiple customers by using centralized security monitoring, tenant separation, correlated authentication alerts, and repeatable investigation and response workflows. A multi-tenant security platform helps providers monitor customer environments while maintaining visibility into each customer's security events and incidents.

Seceon's OTM Platform supports multi-tenant security operations for service providers. Its AI/ML-driven analytics, centralized visibility, and threat detection capabilities can help MSSPs identify suspicious login activity, investigate credential-based attacks, and coordinate response across supported customer environments.

Seceon aiSIEM-CGuard

24/7 Access to Seceon’s Cybersecurity Experts - Because Threats Don’t Wait

Do These Persistent Issues Impact Your Day-to-Day Operations?
  • Large number of failed logins from single/multiple IPs, internal or external, against a single/multiple usernames.
  • Failed logins from new geo locations or a new user device.
  • Large number of account lockouts.
  • High cost of integration, support and maintenance.

    Seceon Inc