Responsive Banner Design

What is Vulnerability Exploits?

A vulnerability is a weakness or flaw in a system, software, or hardware that can be exploited by attackers to gain unauthorized access or cause harm. An exploit is a piece of code or a software tool used by adversaries to take advantage of such vulnerabilities.
Exploits target these vulnerabilities across digital assets to perform unauthorized actions, such as planting malware, Trojans, worms, or bots, or accessing sensitive data. Understanding the relationship between vulnerabilities and exploits is essential for effective cybersecurity management.
By addressing vulnerabilities, organizations can prevent attackers from executing exploits that could lead to data breaches, disruptions, or more severe damages to critical infrastructure.

Challenges

Vulnerability Prioritization Complexities

Prioritizing vulnerabilities is challenging, especially in large organizations with thousands of vulnerabilities requiring attention and resources.

Challenges in Vulnerability Remediation

Addressing vulnerabilities can take weeks or months due to a shortage of security staff and competing priorities across multiple work items.

Evaluating Vulnerability Management Effectiveness

Measuring the success of a vulnerability management program is difficult, as it’s tied to ongoing security and compliance efforts.

Seceon OTM Platform

Spot the exploit attempt, and the one that got through

Exploit detection that reads WAF, server and network activity together, with vulnerability context that tells you what to fix first.

Potential Web Exploit alert

WAF-aware exploit detection

Flags exploit attempts that slip past the WAF, succeed from an internal source, or repeat until something gives.

Illustrative example.

WAF bypass: exploit not handled by the WAF, with an unusual response
Successful exploit: exploit activity from an internal source returns success
Repeated attempts: 5 blocked in 5 minutes, or 20 for high frequency
Potential Exploit Vulnerability alert

Known weaknesses under attack

Raised on exploit patterns, suspicious payloads, or correlation with exposed vulnerabilities on the targeted host.

Exploit patternsSuspicious payloads

NDR

Scanning before the strike

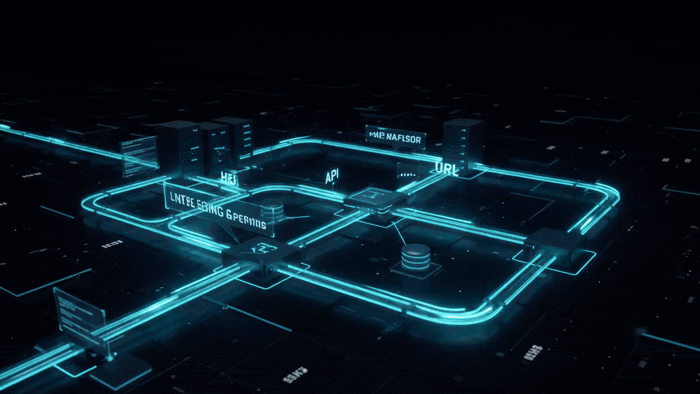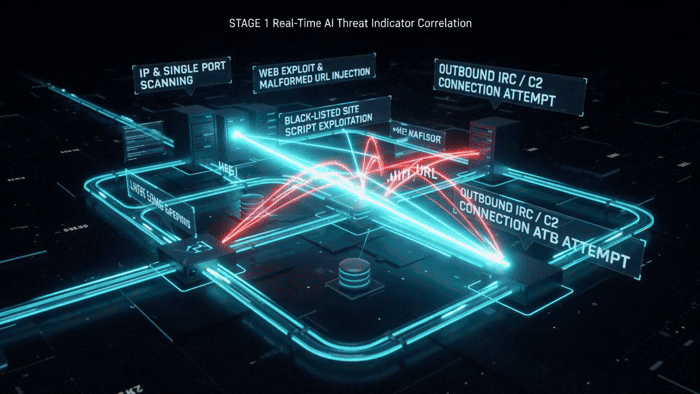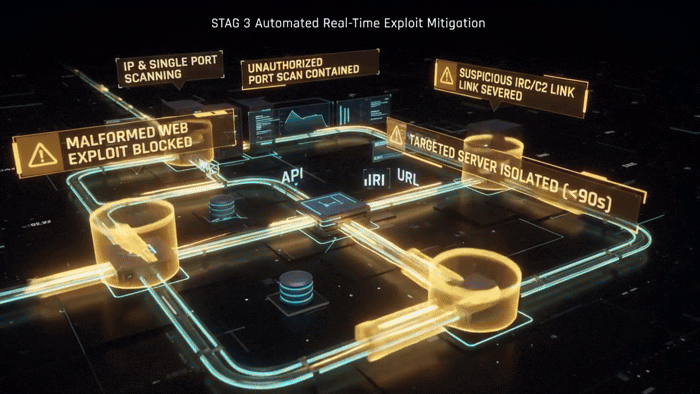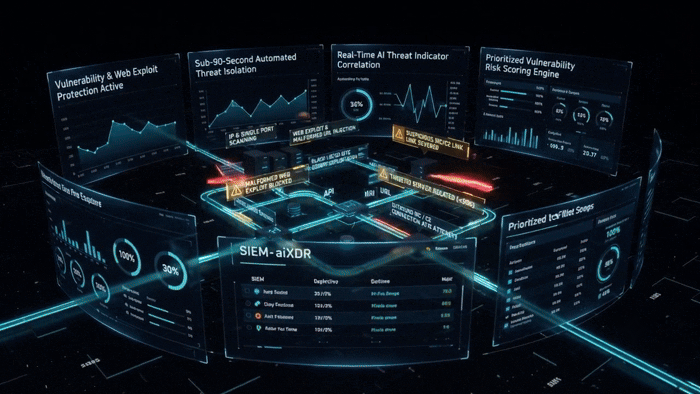
Port scans and probing that often come before an exploit are flagged as behavioral anomalies.

Vulnerability Management

Exploited in the wild

Each CVE is mapped to known threat actors and campaigns. CISA KEV listings are elevated automatically.

CISA KEVCVE to threat actor

Potential Infiltration alert

Early-stage break-in

Correlates exploitation attempts, unusual connections and contact with known malicious sources.

Exploitation attemptsMalicious sources

Risk-based prioritization

Fix what attackers are using, first

A composite risk score ranks the remediation queue. Vulnerabilities on assets with active attack activity are auto-elevated to Critical.

Automated response

<90s

Containment through SOAR

Remediation tracking

From finding to verified fix

Patch tickets are created through SOAR, and a verification scan confirms each vulnerability is closed.

ServiceNowJIRABMC Remedy

aiBAS360

Prove your defenses hold

Simulates real-world attack techniques to find gaps before adversaries exploit them, aligned to MITRE ATT&CK with prioritized remediation guidance.

Attack simulationMITRE ATT&CKPrioritized remediation

Vulnerability Exploits FAQs

Understand how organizations identify exploitation attempts, investigate web attacks, prioritize risks, and strengthen threat detection with Seceon.

What is vulnerability exploit detection, and how is it different from vulnerability scanning?

Vulnerability scanning identifies weaknesses in software, systems, or configurations that attackers could exploit. Vulnerability exploit detection focuses on identifying activity that may indicate an attacker is attempting to take advantage of those weaknesses. Both are important: scanning helps identify exposure, while exploit detection helps security teams recognize active attack attempts.

Seceon addresses exploitation detection through its AI-driven security analytics. Its aiSIEM and aiXDR solutions analyze security indicators to help identify and classify vulnerability exploit and web exploit activity. Seceon also offers vulnerability assessment capabilities to help organizations identify and prioritize weaknesses.

How can security teams detect attempts to exploit open ports and exposed services?

Security teams should monitor repeated IP scans, single-port scans, unusual connection attempts, and unexpected outbound communications from potentially affected systems. A scan does not automatically mean a system has been compromised, so analysts should correlate it with other indicators, such as suspicious processes, threat intelligence matches, and subsequent network connections.

Seceon identifies vulnerability exploit indicators such as IP scanning and single-port scanning. Its security analytics can help correlate these events with other suspicious activity, including connections to potentially malicious external infrastructure. Detection depends on the network telemetry and relevant integrations available to the platform.

How can organizations detect web exploits such as SQL injection and cross-site scripting?

Web exploits can involve crafted URLs, malicious input, unexpected application requests, or attempts to manipulate how an application processes data. SQL injection targets database queries, while cross-site scripting (XSS) attempts to execute malicious scripts in a user's browser. Organizations should monitor application and security logs, investigate suspicious request patterns, and validate protections in the application itself.

Seceon identifies web exploit activity through its Web Application Security use case, with aiSIEM and aiXDR helping security teams analyze relevant indicators and investigate suspicious activity. Detection coverage depends on the telemetry collected and the security controls deployed.

Can AI-powered security tools detect zero-day exploits that have no known signatures?

Zero-day exploits target vulnerabilities for which a patch may not yet be available. Because the exploit or its indicators may be unknown, signature-based detection alone may not be sufficient. Behavioral analytics, anomalous process activity, unusual network connections, and correlation across multiple security events can help identify activity consistent with exploitation.

Seceon uses AI/ML-driven behavioral analytics and Dynamic Threat Modeling to help identify suspicious activity associated with emerging threats. Its zero-day threat detection approach complements vulnerability exploit monitoring. No detection method can guarantee identification of every zero-day exploit.

How should businesses prioritize vulnerabilities when they have thousands of security issues to fix?

Businesses should consider more than the number or severity score of reported vulnerabilities. Prioritization should account for exploit activity, asset criticality, exposure to the internet, potential business impact, available patches, and existing compensating controls. This helps teams focus limited remediation resources on weaknesses that pose the greatest practical risk.

Seceon helps security teams analyze vulnerability exploit indicators and classify detected exploit activity as critical or major alerts based on the available threat indicators. Its vulnerability assessment capabilities can also help organizations identify and prioritize vulnerabilities. Remediation priorities should be validated against the organization's asset inventory and risk management process.

How can organizations respond to vulnerability exploitation attempts in real time?

Organizations should validate the alert, determine which systems are affected, and assess whether exploitation succeeded. Depending on the incident, response may include blocking malicious traffic, isolating a compromised endpoint, applying a security patch, disabling an exposed service, and investigating related activity to identify possible lateral movement or data access.

Seceon's OTM (Open Threat Management) Platform brings together security event analytics and response capabilities through aiSIEM and aiXDR. It helps teams correlate exploitation indicators, investigate incidents, and support response workflows. Available response actions depend on the connected tools, integrations, and automation policies configured in each environment.

Summary Section

Summary

Seceon’s AI-powered solution detects and prevents vulnerability exploits by continuously monitoring system activity, identifying potential exploitation attempts in real-time, and automatically mitigating risks to ensure comprehensive protection against known and emerging vulnerabilities.

Seceon aiSIEM-CGuard

24/7 Access to Seceon’s Cybersecurity Experts - Because Threats Don’t Wait

Do These Persistent Issues Impact Your Day-to-Day Operations?
  • Large number of failed logins from single/multiple IPs, internal or external, against a single/multiple usernames.
  • Failed logins from new geo locations or a new user device.
  • Large number of account lockouts.
  • High cost of integration, support and maintenance.

    wpChatIcon
    wpChatIcon