See how aiBAS360 validates security controls by simulating adversary behaviors across abilities, operations, and threat-informed scenarios.
Most organizations assume their security stack detects the threats it's supposed to — but that assumption is rarely tested. A traditional penetration test is a point-in-time snapshot that goes stale within weeks, while new attack techniques and configuration drift quietly open new gaps.
Without
continuous, automated validation
against real-world adversary techniques, boards and regulators are left with an assumed security posture instead of an evidence-backed one.
Validate your defenses every day against evolving threats. Instead of waiting for annual audits, aiBAS360 runs nonstop, giving you real-time insight into whether your investments are truly working.
Our AI engines replicate the latest hacker tactics including phishing, privilege escalation, lateral movement and data exfiltration safely inside your environment. This reveals blind spots traditional tools miss.
Automatically generate detailed evidence for frameworks like NIST, ISO 27001, PCI-DSS and HIPAA. Save weeks of audit preparation and give executives confidence in measurable resilience.
aiBAS360 continuously simulates real-world cyberattacks, validates your security controls, identifies gaps across your environment, and provides actionable intelligence to strengthen your defenses and improve cyber resilience.
Build a clear picture of your security environment. aiBAS360 identifies endpoints, users, applications, networks, cloud resources, security controls and potential attack paths that adversaries could exploit.
Safely execute realistic attack scenarios modeled after modern adversaries, including ransomware, phishing, credential attacks, privilege escalation, lateral movement, insider threats and data exfiltration techniques.
Test how your defenses respond when an attacker attempts to compromise the environment. Simulations can evaluate endpoint controls, identity defenses, network security, cloud controls and SOC detection capabilities.
Measure whether your existing security controls actually detect, block and respond to simulated attacks. aiBAS360 identifies missed detections, ineffective controls, security gaps and weaknesses across the attack chain.
Receive prioritized recommendations based on identified weaknesses. Connect findings with aiSIEM and aiXDR workflows to improve detection, strengthen SOC playbooks and accelerate security remediation.
aiBAS360 adapts breach and attack simulation to the priorities of service providers, security leaders, and SOC teams — helping every team validate and strengthen its security posture.
Turn breach and attack simulation into a scalable security service that helps differentiate your offering and create recurring customer value.
Translate technical security validation into measurable business outcomes, risk visibility, and executive-level insight.
Continuously test defensive readiness, expose detection gaps, and strengthen the ability of security teams to respond to real-world attack techniques.
aiBAS360 provides continuous validation of defenses through scalable automation, adaptive attack paths and end-to-end coverage across network, cloud, endpoint and identity.
Annual or quarterly penetration tests leave long gaps between security validation cycles.
Expensive per-engagement testing provides limited ongoing coverage and ROI.
Manual attack scenarios are limited and not adaptive to new threats.
Standalone tools provide no direct remediation linkage.
Manual evidence gathering creates a high audit burden.
AI-Driven Security
Validation
Continuous, 24/7 validation of defenses replaces long gaps between testing cycles.
Scalable automation lowers ongoing cost while supporting continuous security validation.
Coverage extends across network, cloud, endpoint and identity.
AI-driven, adaptive validation uses real-world attack paths.
Seamlessly works with aiSIEM & aiXDR for remediation.
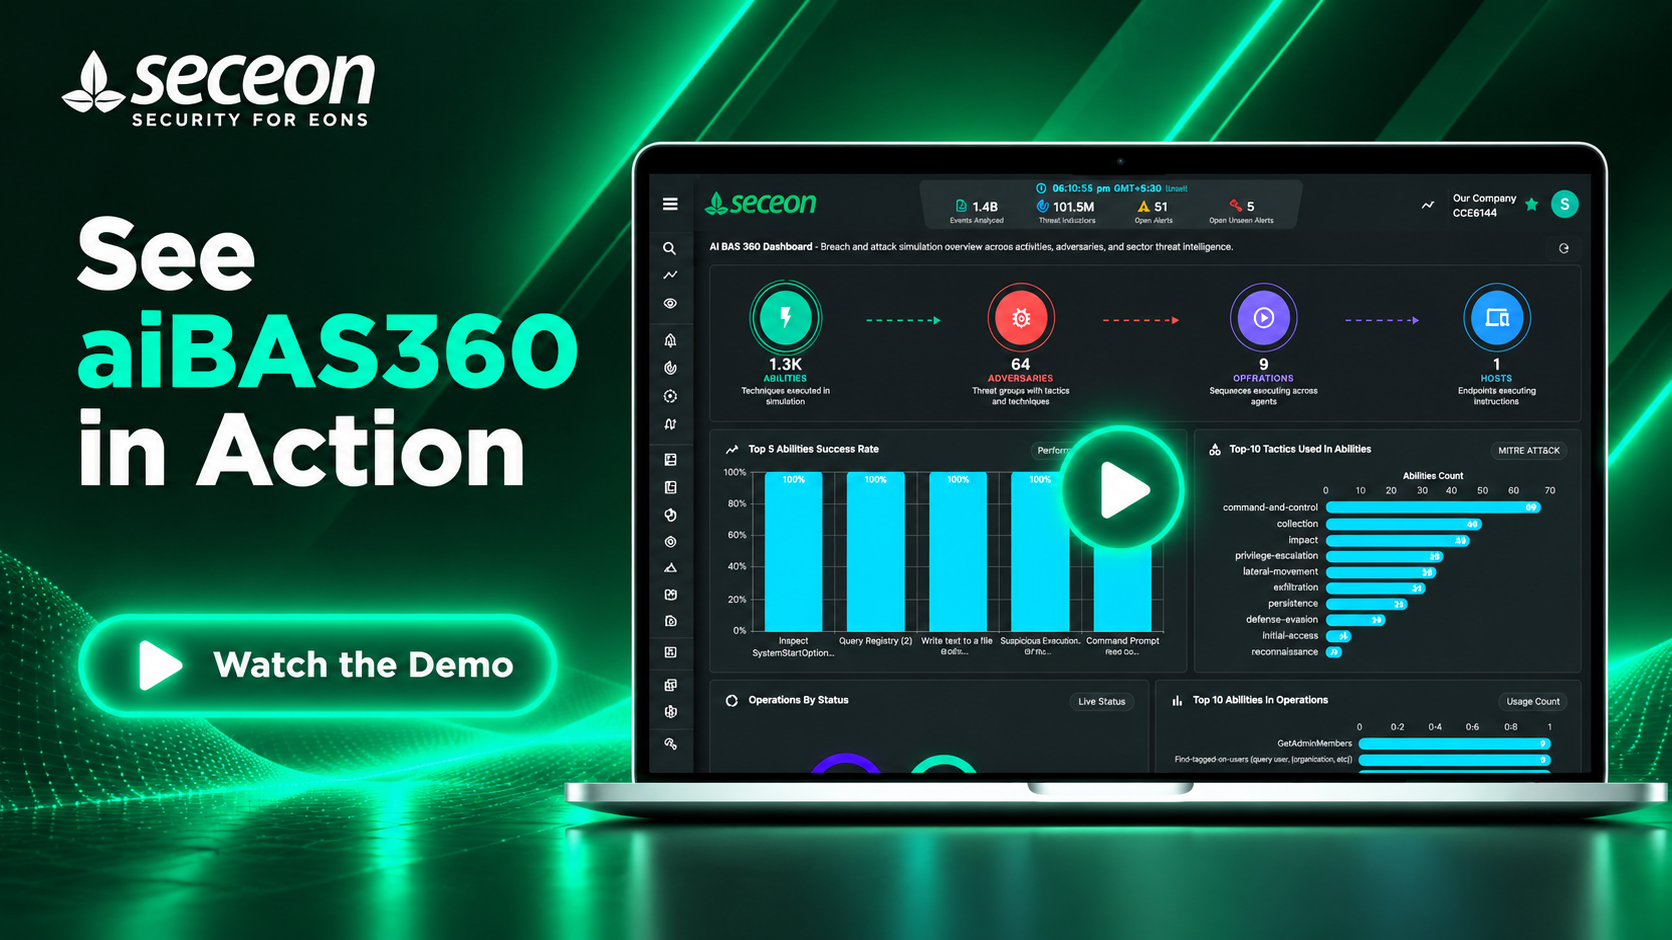
See how aiBAS360 continuously validate security controls, simulate real-world attacks, identify exploitable gaps, and strengthen your security posture.
Get clear answers about how Seceon aiBAS360 continuously validates security controls against real-world attack techniques, before adversaries find the gaps.
Seceon aiBAS360 is a Breach and Attack Simulation module that continuously validates whether your security platform actually detects the threats it claims to detect. Unlike a periodic penetration test or annual red team exercise, which only tests a single point in time, aiBAS360 runs ongoing simulated attacks against your live environment using real-world MITRE ATT&CK techniques, so detection gaps are found and closed continuously rather than once a year.
Yes. aiBAS360 uses a safe simulation methodology that causes no disruption to production systems, while covering the full attack lifecycle from initial access through execution, persistence, lateral movement, and exfiltration. This allows continuous testing against live infrastructure without the operational risk of a live red team engagement.
Yes. aiBAS360 maps every simulation result against MITRE ATT&CK v14+ across the Enterprise, ICS, and Containers matrices, and generates a real time coverage heatmap that updates continuously as new simulations run. This gives security teams a clear, evidence based view of exactly which attack techniques are and are not currently detected.
aiBAS360 generates an automated detection gap alert with specific remediation guidance, prioritized by threat relevance and asset exposure. Once a fix is applied, aiBAS360 automatically re-runs the simulation to confirm the gap has actually been closed, rather than assuming the fix worked.
Yes. aiBAS360 measures actual detection rate against assumed coverage, distinguishing between having a detection rule written for a technique and that rule actually triggering a real alert when the attack happens. It also measures mean time to respond (MTTR) for each detected simulated attack, giving a true picture of operational readiness rather than paper coverage.
aiBAS360 is natively integrated with aiSIEM, so simulated attacks generate real alerts inside the same detection pipeline used for genuine threats. This means validation happens against the actual production detection logic your SOC relies on, not a separate testing sandbox disconnected from day to day operations.
Copyright @Seceon Inc 2026. All Rights Reserved.
