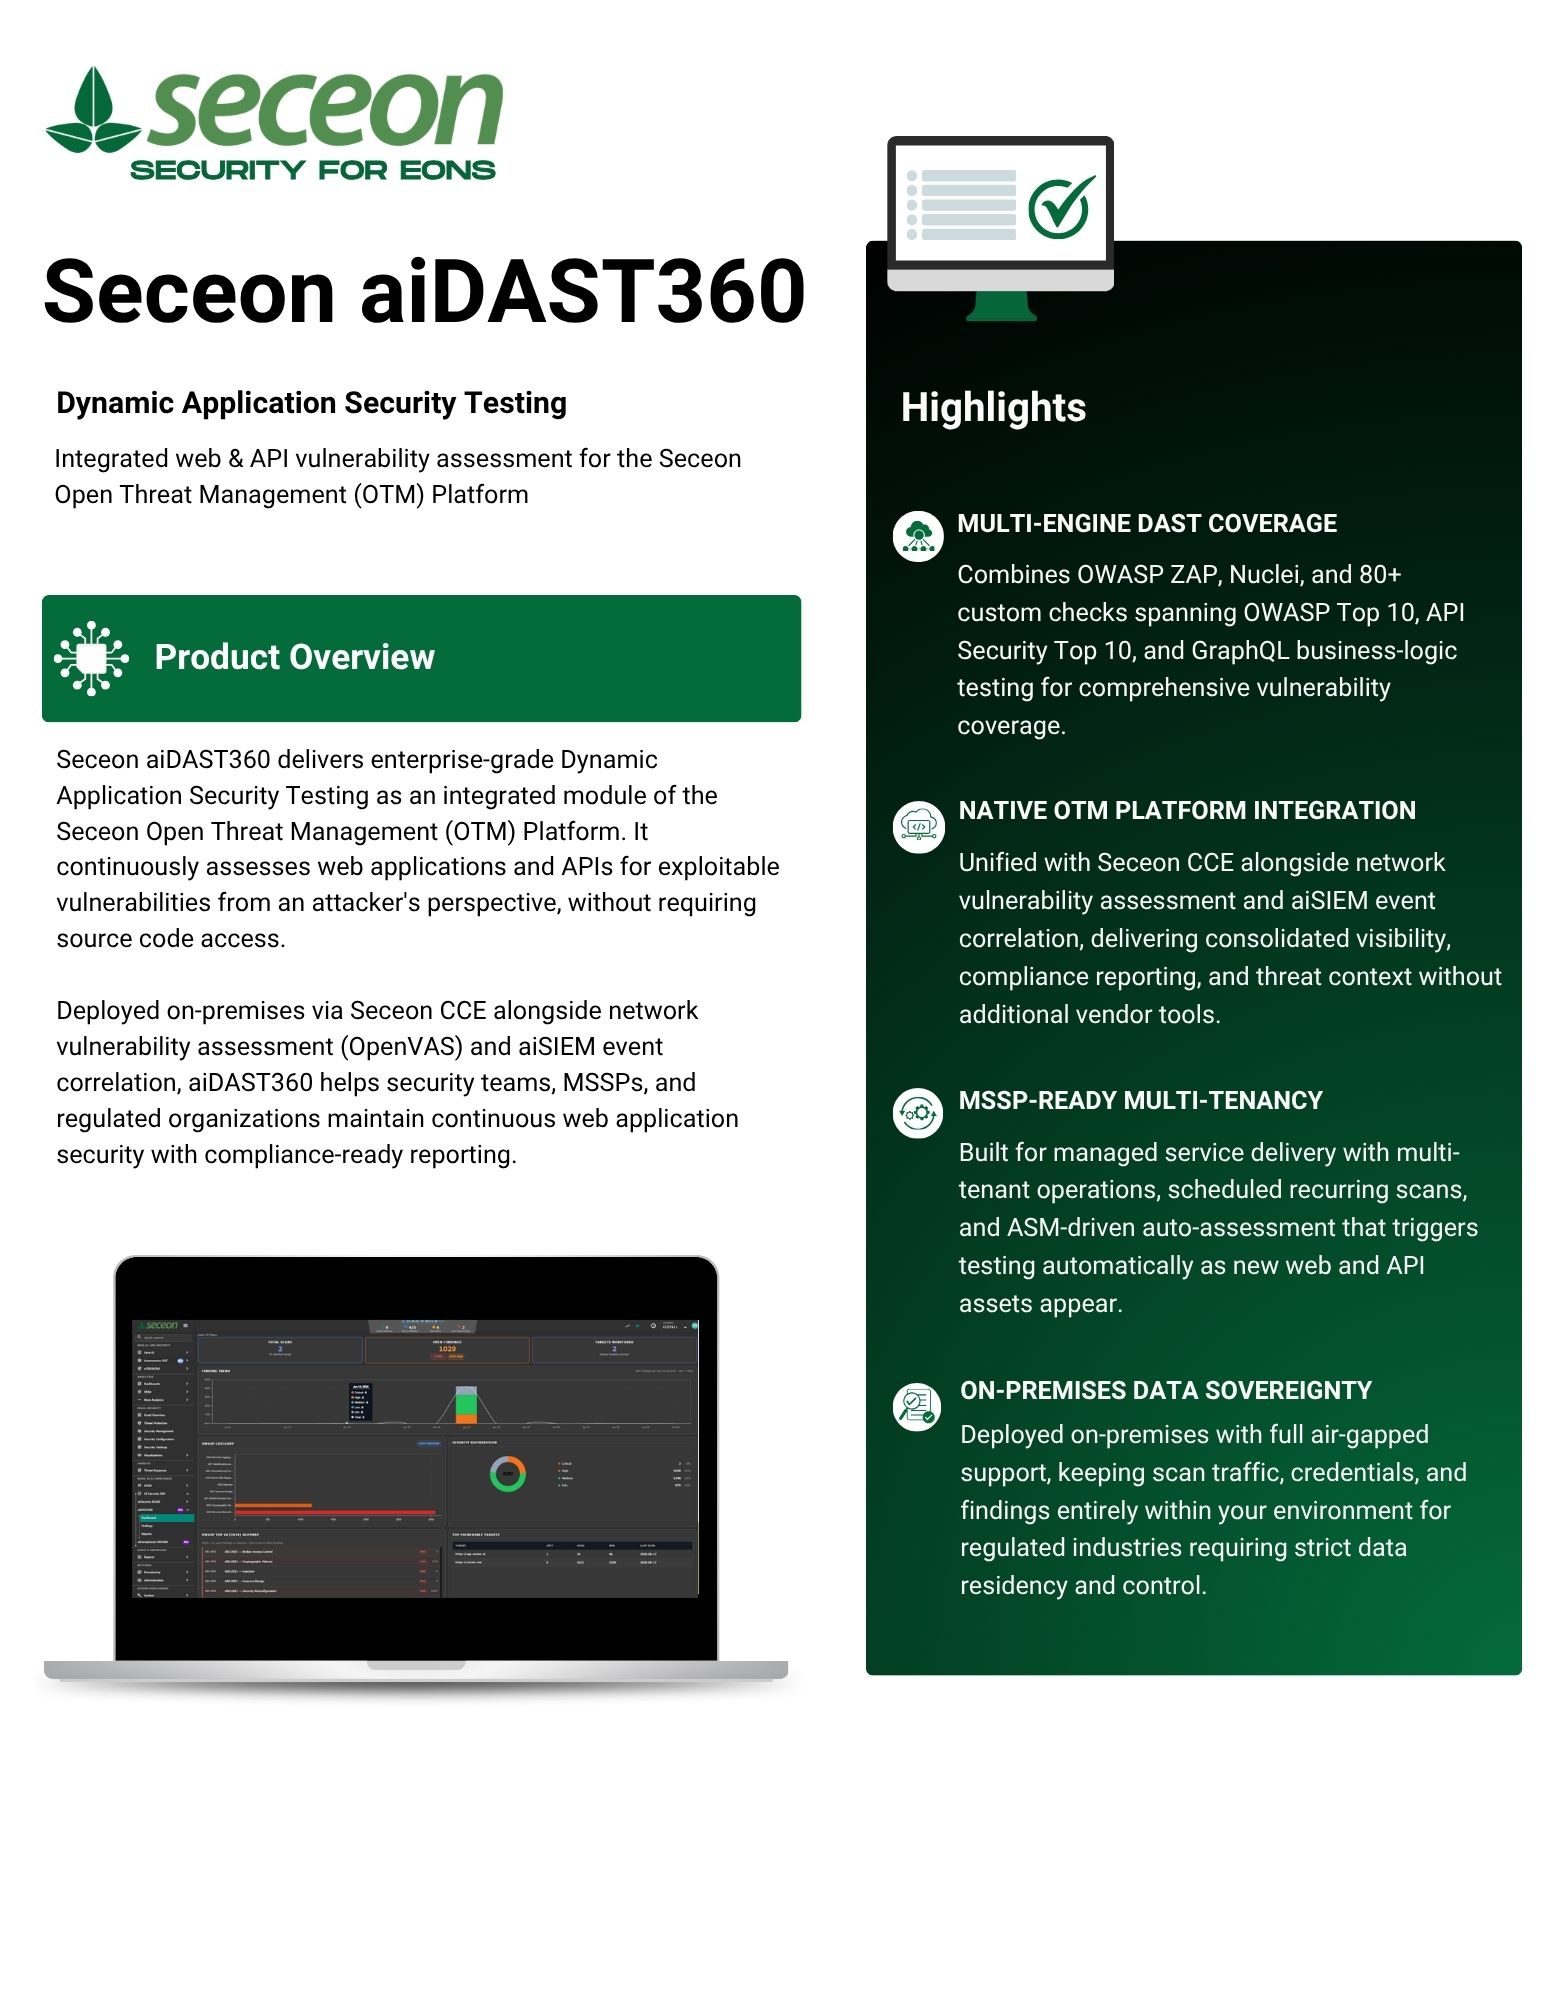
aiDAST360

See Application Security In Action.

See how aiDAST360 discovers vulnerabilities, prioritizes risk, and helps teams secure web applications and APIs.
  • Scan web applications and APIs.
  • Prioritize critical security risks.
  • Investigate vulnerable assets and endpoints.
  • Track remediation and security reports.
Request Demo Interactive product walkthrough
Interactive aiDAST360 Demo Hover on any section or dashboard item to know more
☰
Our Company CCE6144
S
APPLICATION SECURITY VIEW

Hover another section to explore it.
APPLICATION / LOGIN DASHBOARD USER APPLICATION LOGIN API RISK aiDAST360 ACTIVE SCANNING API GATEWAY REST / OPENAPI AUTHENTICATED USER SERVICE REST API PAYMENT SERVICE DATA SERVICE DATABASE API ACCESS CONTROL API EXPOSURE BUSINESS LOGIC SECEON OTM THREAT CORRELATION

The Application Security Blind Spot

Modern web applications and APIs constantly change, creating new security risks that traditional controls can miss. Vulnerabilities such as injection, access control flaws, exposed APIs, and insecure configurations can remain hidden without continuous testing.

aiDAST360 dynamically tests applications and APIs to identify vulnerabilities, reduce false positives, and prioritize risks for faster remediation.

!
Web Vulnerabilities
↗
API Security
◉
Dynamic Testing
✓
Risk & Compliance
Can you see the vulnerabilities across your applications and APIs?
How Seceon aiDAST360 Works

What aiDAST360 Does

01
Application Discovery

Discover

  • Automatically discover web applications, APIs, endpoints, and exposed attack surfaces so security teams can understand what needs to be tested.
02
Dynamic Security Testing

Test

  • Perform dynamic security testing against applications and APIs using automated vulnerability checks to uncover weaknesses that attackers could exploit.
03
Risk Prioritization

Prioritize

  • Turn discovered vulnerabilities into actionable findings with severity, evidence, and remediation context so teams can focus on the risks that matter most.
How aiDAST360 Works
Dynamic Application Security Testing

How aiDAST360 Works

aiDAST360 continuously evaluates web applications and APIs to uncover weaknesses, validate risk, and help security teams move from detection to remediation faster.

1

Discover

Map applications, APIs, endpoints, services, and exposed entry points across the attack surface.

2

Scan

Run dynamic security tests against live application behavior to expose exploitable weaknesses.

3

Detect

Identify application and API vulnerabilities, security gaps, and configuration weaknesses.

4

Validate

Enrich findings with evidence, severity, confidence, affected locations, and context.

5

Remediate

Prioritize actionable findings so security and development teams can fix what matters most.

Application Attack Surface
Map exposed components, URLs, API routes, and services for a clearer view of externally reachable assets.
Security Coverage
Assess application behavior against recognized security categories, including OWASP-aligned and API risks.
Remediation Intelligence
Give security and development teams a focused view of affected assets, severity, evidence, and priorities.
Tailored to Your Needs - aiDAST360
Built Around Your Security Role

Tailored to Your Needs

aiDAST360 delivers focused application security intelligence for every team responsible for protecting your digital environment.

01

For Development Teams

Bring application security closer to development and resolve vulnerabilities before they reach production.

  • Identify vulnerabilities before they reach production.
  • Get clear findings with evidence to speed up remediation.
  • Integrate application security testing into development workflows.
Developer Security
02

For Security Teams

Gain continuous application visibility, prioritize meaningful risk and strengthen security coverage.

  • Maintain continuous visibility across web applications and APIs.
  • Prioritize high-impact vulnerabilities using severity and context.
  • Strengthen application security coverage with automated testing.
Security Operations
03

For CISOs & Security Leaders

Turn application security data into strategic visibility, measurable progress and actionable leadership insight.

  • Gain a consolidated view of application security posture.
  • Track vulnerability trends and remediation progress.
  • Support security and compliance reporting with actionable findings.
Executive Security
The aiDAST360 Difference

Security Gaps In. Actionable Security Out.

aiDAST360 acts as the central security layer between application security challenges and the actions teams need to take.

Security Gaps
Security Engine
aiDAST360 Outcomes

Fragmented Visibility

Security teams struggle to maintain a clear view across applications, APIs, endpoints and attack surfaces.

Testing Gaps

Disconnected tools and testing processes create duplicated effort, blind spots and inconsistent coverage.

Security Noise

Large volumes of findings make it difficult to identify vulnerabilities that deserve immediate attention.

Risk Prioritization

Technical findings often lack the context needed to connect risk with remediation and compliance.

Active Security Engine

aiDAST360

Dynamic Application
Security Intelligence

Application Discovery
Dynamic Security Testing
AI-Assisted Analysis
Risk Prioritization
Compliance Intelligence

Continuous Visibility

Discover and map applications, APIs, endpoints, services and exposed attack surfaces.

Unified Testing

Streamline dynamic security testing across web applications and APIs through one workflow.

Intelligent Findings

Enrich findings with context, evidence, severity, confidence and actionable prioritization.

Risk to Compliance

Connect OWASP, CWE, CVEs, severity and compliance frameworks into actionable reporting.

Seceon Solutions
Seceon aiDAST360 Datasheet

Discover More with Our Datasheet

Explore how Seceon aiDAST360 provides continuous Dynamic Application Security Testing across web applications, APIs, and enterprise application environments.

Discover how aiDAST360 identifies vulnerabilities, validates security findings, prioritizes application risks, and supports compliance-ready security reporting.

Frequently Asked Questions

Get clear answers about how Seceon aiDAST helps organizations discover application and API vulnerabilities, validate security risks, prioritize remediation, and strengthen application security.

What is DAST (Dynamic Application Security Testing) and how does Seceon aiDAST work?

DAST, or Dynamic Application Security Testing, tests running web applications and APIs from the outside to identify vulnerabilities that attackers could exploit. Unlike source-code-based testing, DAST evaluates application behavior in a live or test environment.

Seceon aiDAST is an AI-powered DAST solution that discovers applications, APIs, endpoints, and exposed attack surfaces, dynamically tests them for security weaknesses, validates findings with evidence and context, and helps security teams prioritize remediation.

What vulnerabilities does Seceon aiDAST detect?

Seceon aiDAST identifies application and API security vulnerabilities across common web application and API attack surfaces, including risks aligned with OWASP security categories. It helps security teams identify issues such as injection vulnerabilities, access-control weaknesses, exposed APIs, insecure configurations, and other application security gaps.

Findings are enriched with severity, confidence, evidence, affected locations, and remediation context so teams can focus on the vulnerabilities that require attention.

Does Seceon aiDAST support API security testing?

Yes. Seceon aiDAST provides dynamic security testing for web applications and APIs, including API discovery, exposed attack-surface mapping, and testing for API-related security risks.

This is particularly relevant for modern application environments that rely on APIs, microservices, and externally exposed application endpoints.

What is the difference between DAST and SAST?

DAST and SAST test applications from different perspectives. DAST tests a running application from the outside and focuses on vulnerabilities in application behavior, endpoints, configurations, and runtime exposure. SAST analyzes source code or other static representations of an application to identify potential security weaknesses.

Seceon aiDAST focuses on dynamic application and API security testing, helping organizations identify vulnerabilities that are exposed during application execution.

Does Seceon aiDAST help with vulnerability prioritization and remediation?

Yes. Seceon aiDAST goes beyond vulnerability discovery by providing severity, confidence, evidence, and affected-location context for identified findings.

This helps security and development teams understand which application vulnerabilities need attention and move from detection and validation toward prioritized remediation.

How does Seceon aiDAST fit into Seceon's cybersecurity platform?

Seceon aiDAST is the Application Security capability within Seceon's broader cybersecurity platform. It brings application and API security visibility into the same environment that includes SIEM, XDR, SOAR, UEBA, and threat intelligence.

This helps organizations connect application security findings with their broader cybersecurity operations instead of managing DAST as a completely separate function.

Seceon aiSIEM-CGuard

24/7 Access to Seceon’s Cybersecurity Experts - Because Threats Don’t Wait

Do These Persistent Issues Impact Your Day-to-Day Operations?
  • Large number of failed logins from single/multiple IPs, internal or external, against a single/multiple usernames.
  • Failed logins from new geo locations or a new user device.
  • Large number of account lockouts.
  • High cost of integration, support and maintenance.

    Seceon Inc