Responsive Banner Design

What is Network Detection and Response (NDR)?

Network Detection and Response (NDR) is a proactive cybersecurity approach designed to identify and counter cyber threats by continuously monitoring network traffic. NDR solutions utilize advanced technologies like machine learning, AI, and behavioral analytics to detect anomalies that may indicate the presence of threats.
By cutting detection and response times by up to 70%, NDR strengthens an organization's ability to respond swiftly to incidents, reducing the risk of data breaches.

Challenges

Complexity of Modern Networks

The growing complexity of IT environments spanning cloud services, remote work, and OT/IoT environments expands the attack surface and complicates visibility, challenging NDR solutions to monitor and detect threats effectively.

False Positives and Alert Fatigue

NDR systems often produce numerous false positives, leading to alert fatigue and risking the oversight of critical threats, which undermines detection and response efficacy.

Integration Challenges

Seamlessly integrating NDR with existing security tools like SIEM and EDR is crucial yet often resource-intensive and complex, posing a significant barrier for many organizations.

Seceon NDR

Network visibility without a single agent

Passive detection and response across north-south, east-west and cloud VPC traffic, correlated with the rest of your security data in aiSIEM.

Passive deployment

Full-packet visibility, zero disruption

Deploys passively through an inline tap, SPAN port or network TAP, with no agents on endpoints.

Protocols include HTTP/S, DNS, SMTP, SMB, RDP, SSH, FTP, SQL, OPC-UA and Modbus, plus 100+ more.

0Agents required
<5 minMean time to detect

East-west

Lateral movement

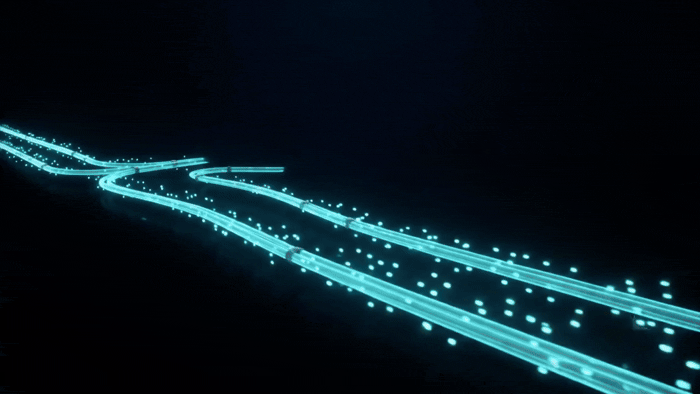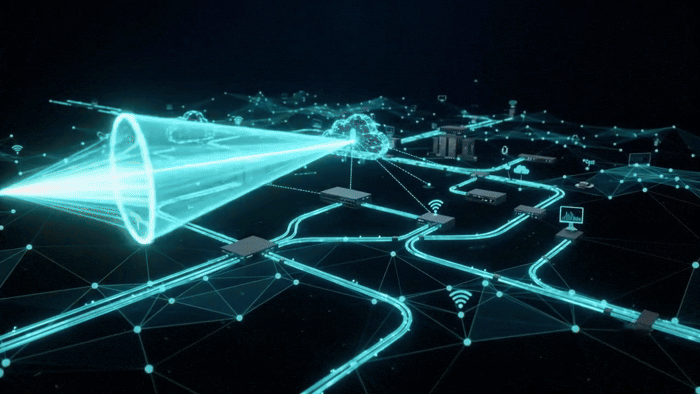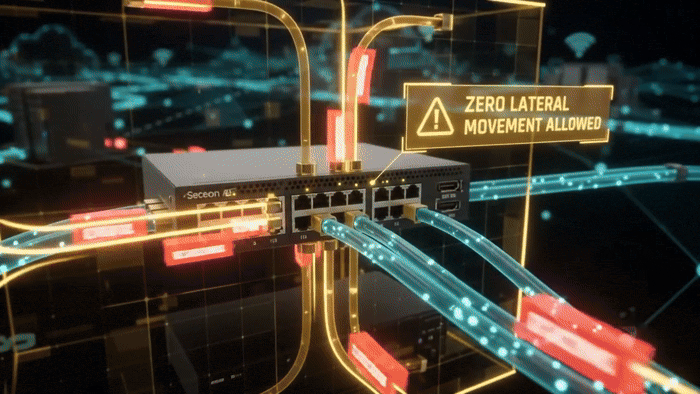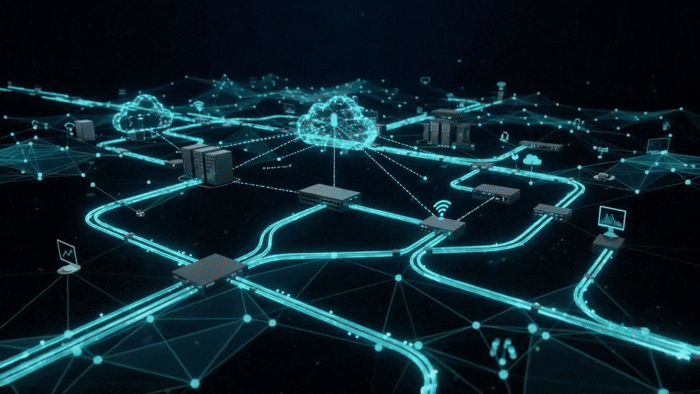
Catches attackers who have bypassed the firewall, using peer-group traffic baselines.

VLAN boundary violationsMicrosegment violations

C2 and DGA

Command-and-control

Frequency and timing analysis exposes covert beaconing and DGA domains.

Encrypted traffic analysis

Threats in TLS, no decryption

Detects anomalies in encrypted traffic without decrypting it, including self-signed, expired and mismatched certificates.

JA3/JA3S fingerprintingCertificate anomalies

Behavioral scoring

Anomaly score per entity

Flags port scans, brute force, data staging and exfiltration patterns.

Unified correlation

Network findings, correlated with logs and identity

Every NDR finding feeds the aiSIEM correlation engine in the same event format, enriched with UEBA risk context.

Automated response

<90s

Containment through SOAR

MITRE ATT&CK

Coverage across key tactics

Network detections map to the tactic categories attackers rely on after initial access.

Lateral MovementCommand and ControlExfiltrationDiscoveryCredential Access

OT/ICS and multi-site

Visibility where agents cannot go

Passive monitoring for OT/ICS segments and legacy devices, with distributed sensors across geographic zones.

OPC-UAModbusDistributed sensorsNo operational disruption

Network Detection and Response FAQs

Learn how AI-driven network detection, behavioral baselining, encrypted traffic analysis, and automated response help organizations detect lateral movement, command-and-control activity, and other network threats with Seceon.

What is Network Detection and Response (NDR), and how does it detect threats that endpoint and perimeter tools miss?

Network Detection and Response (NDR) is a proactive cybersecurity approach that continuously monitors network traffic and uses machine learning, AI, and behavioral analytics to identify anomalies that may indicate a threat. Because it analyzes traffic itself, NDR can reveal attacker activity that bypasses perimeter controls or occurs on devices where endpoint agents cannot be installed. NDR can help reduce detection and response times by up to 70%, though results vary by environment.

Seceon NDR delivers real-time detection, analysis, and response to network threats through aiSIEM and aiXDR. It uses deep packet inspection, behavioral baselining, and protocol anomaly detection across north-south, east-west, and cloud VPC traffic. Actual detection coverage depends on traffic visibility, sensor placement, and configuration.

What are the best agentless NDR solutions for enterprises, including OT/ICS environments, in 2026?

The best NDR solution depends on an organization's network architecture, traffic volume, hybrid and cloud footprint, OT/IoT exposure, and integration needs. Enterprises should evaluate solutions based on passive deployment options, supported traffic sources, protocol coverage, behavioral detection, SIEM and EDR integration, and response automation. Agentless monitoring is especially important for OT/ICS segments and legacy devices where agents cannot be installed.

Seceon NDR deploys passively through an inline tap, SPAN port, or network TAP with no agents on endpoints. It accepts full-packet capture, NetFlow v5/v9, IPFIX, sFlow, and PCAP replay, and covers protocols including HTTP/S, DNS, SMTP, SMB, RDP, SSH, FTP, SQL, OPC-UA, and Modbus, plus 100+ more. Distributed sensors support multi-site and geographically distributed networks. Organizations should validate sensor placement and supported data sources for their own environment before deployment.
How can I detect lateral movement and east-west attacks that have already bypassed the firewall?

Organizations can detect lateral movement by monitoring east-west traffic between internal systems, building peer-group traffic baselines, and flagging deviations such as unusual protocol use, unexpected connections between segments, port scans, and credential-based activity. Perimeter firewalls typically cannot see this internal traffic, so internal network visibility is essential.

Seceon NDR catches attackers who have bypassed the firewall by using peer-group traffic baselines, and it detects VLAN boundary violations and microsegment violations. Its network detections map to MITRE ATT&CK tactics including Lateral Movement, Discovery, and Credential Access. Detection effectiveness depends on east-west traffic visibility and how the network is instrumented.

How can organizations detect command-and-control beaconing, DGA domains, and threats hidden in encrypted TLS traffic?

Organizations can detect command-and-control (C2) activity by analyzing the frequency and timing of connections to expose covert beaconing and algorithmically generated (DGA) domains. For encrypted traffic, metadata-based techniques such as TLS fingerprinting and certificate analysis can reveal suspicious behavior without decrypting the traffic.

Seceon NDR uses frequency and timing analysis to expose covert beaconing and DGA domains, and detects anomalies in encrypted traffic without decryption, including self-signed, expired, and mismatched certificates, using JA3/JA3S fingerprinting and certificate anomaly detection. Results depend on the visibility of the monitored traffic and the attacker technique used.

Which NDR solutions correlate network findings with SIEM logs and identity data to reduce false positives and alert fatigue?

NDR solutions that integrate with SIEM and identity analytics can reduce alert fatigue by correlating network findings with logs, user behavior, and risk context instead of presenting each alert in isolation. When evaluating a platform, organizations should examine data format consistency, correlation capabilities, behavioral scoring, UEBA integration, and investigation workflows.

Seceon NDR feeds every network finding into the aiSIEM correlation engine in the same event format, enriched with UEBA risk context, so network findings are correlated with logs and identity data. It also assigns each entity a composite anomaly score from 0 to 100, shared with UEBA risk scoring, to help flag port scans, brute force, data staging, and exfiltration patterns. Actual false-positive reduction depends on telemetry quality and tuning.

Which NDR solutions can automatically contain network threats by isolating hosts, blocking traffic, and sinkholing malicious DNS?

Organizations looking for automated network containment should evaluate NDR platforms that combine detection with orchestrated response actions, such as isolating compromised hosts, injecting firewall block rules, and sinkholing malicious DNS. Automated containment can shorten the window between detection and response, but it should include approval controls and auditability.

Seceon NDR supports containment through SOAR, including isolating the host, injecting a firewall block rule, and sinkholing malicious DNS, with automated response in under 90 seconds. It also reports a mean time to detect of under 5 minutes. Organizations should confirm which response actions and integrations are available for their specific deployment before implementation.

Summary Section

Summary

Seceon’s AI-driven NDR solution continuously monitors network traffic, detecting and analyzing anomalies in real-time. It identifies potential threats using advanced machine learning models and automatically responds to neutralize risks, providing comprehensive protection against evolving cyber threats.

Seceon aiSIEM-CGuard

24/7 Access to Seceon’s Cybersecurity Experts - Because Threats Don’t Wait

Do These Persistent Issues Impact Your Day-to-Day Operations?
  • Large number of failed logins from single/multiple IPs, internal or external, against a single/multiple usernames.
  • Failed logins from new geo locations or a new user device.
  • Large number of account lockouts.
  • High cost of integration, support and maintenance.

    wpChatIcon
    wpChatIcon