Instant Compliance Readiness
Maps existing controls across 20+ compliance frameworks using accumulated SIEM data and security telemetry, completing up to 80% of requirements from day one.
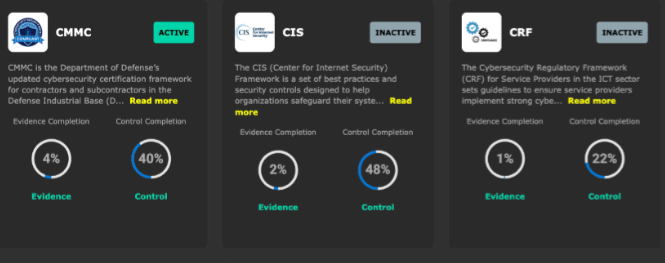
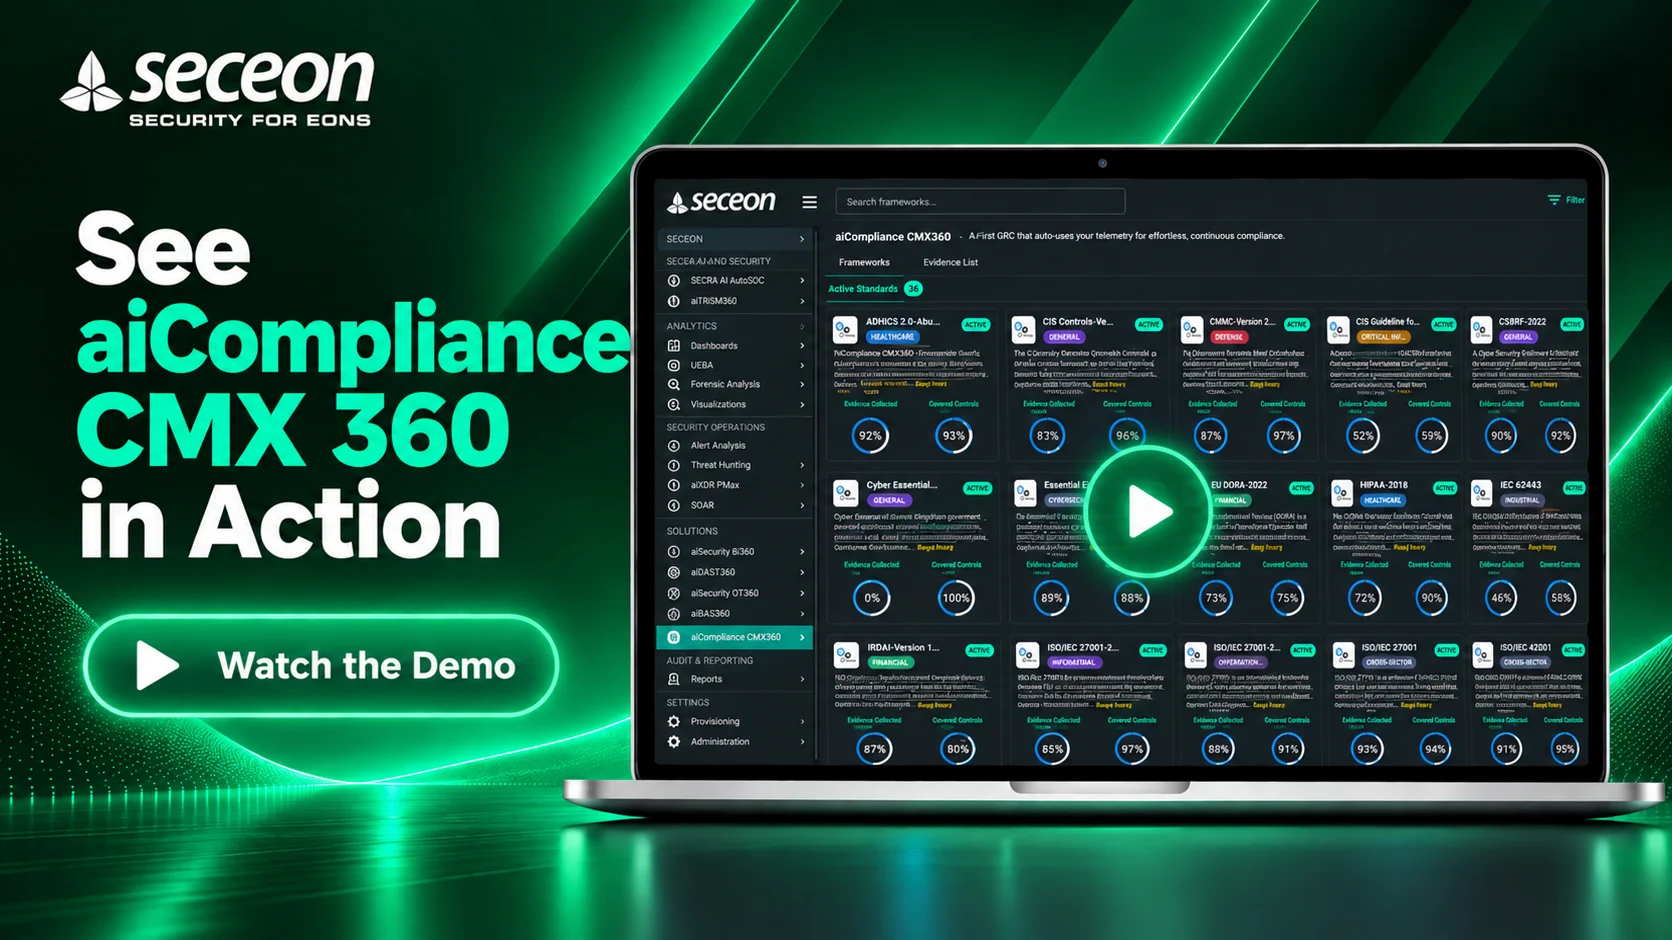
Explore an interactive aiCompliance CMX360 dashboard and see how existing security telemetry becomes continuous compliance evidence across frameworks, controls and audit requirements.
☰
Unified visibility and real-time readiness across all cybersecurity frameworks.
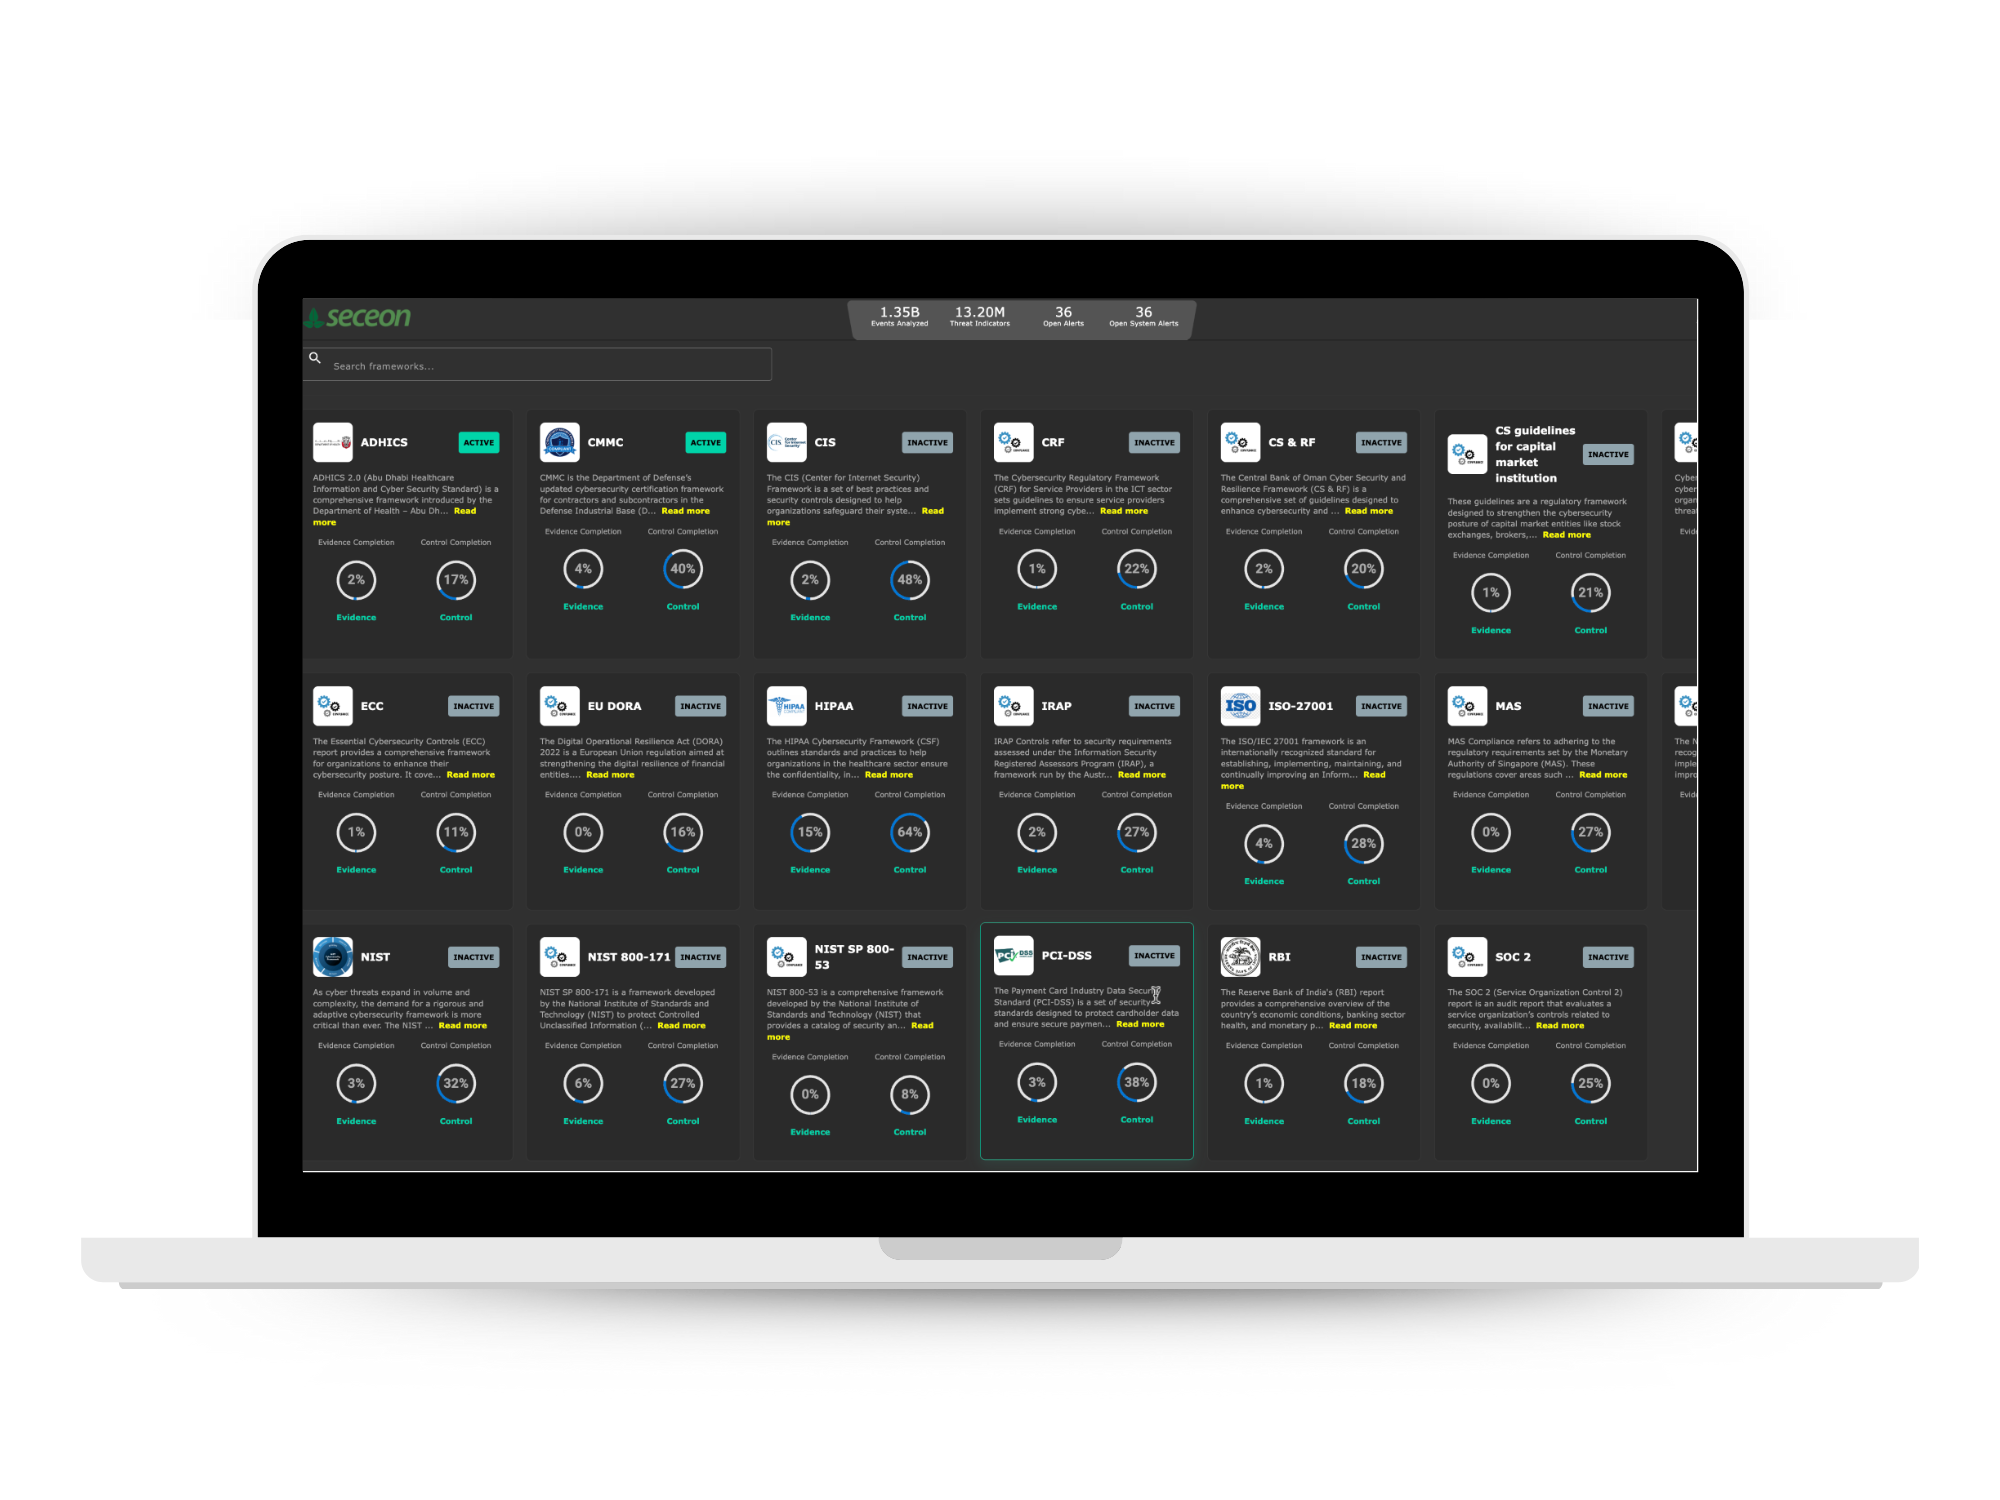
The dashboard automatically gathers compliance evidence from your existing security posture, cutting down the time and effort needed to prepare for audits.
Shows necessary controls that have been implemented according to the framework's requirements. A higher percentage means closer to full implementation of security controls.
The platform tracks your progress across multiple frameworks like SOC 2, ISO 27001, HIPAA, NIST 800-171, PCI DSS, and more, all in one place.
Along with compliance tracking, the dashboard continuously monitors and validates security events.
CMX360 transforms real security intelligence into continuous compliance readiness, helping organizations reduce manual effort, improve visibility, and stay prepared for audits.
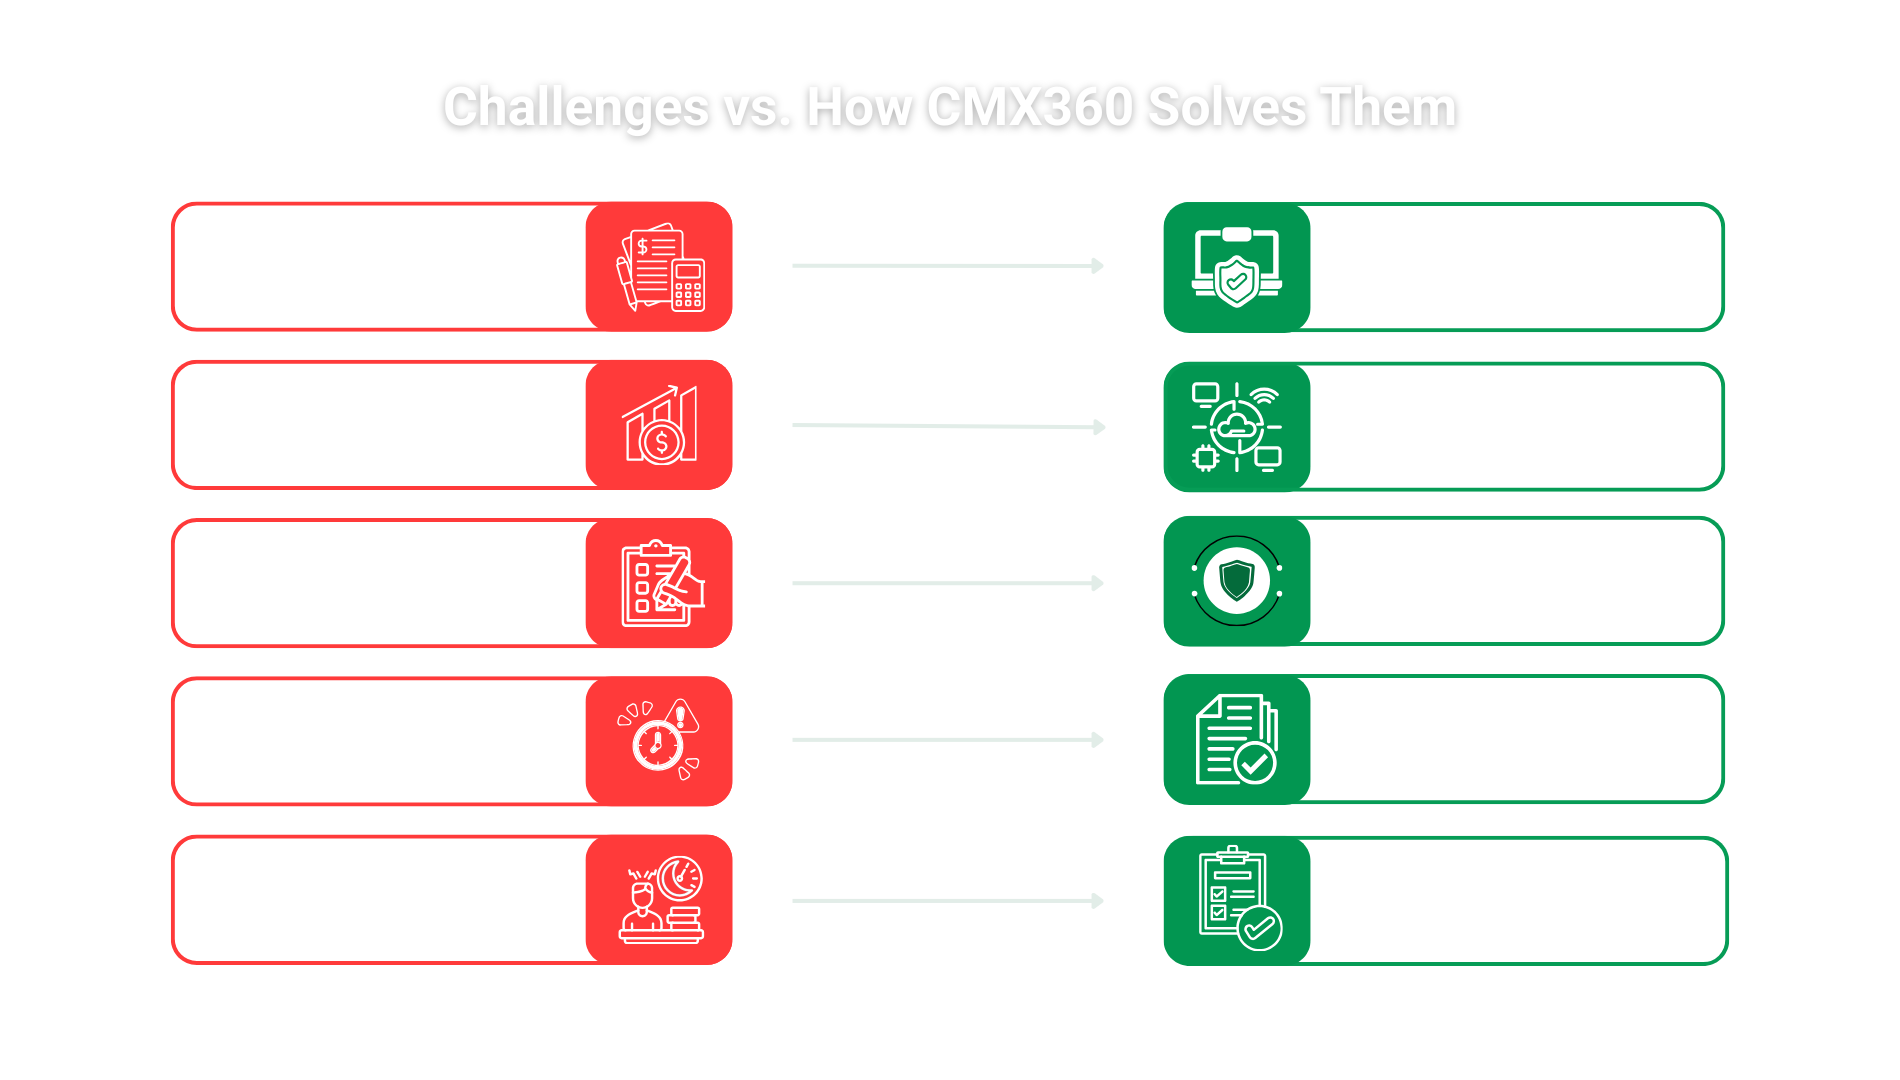
Maps existing controls across 20+ compliance frameworks using accumulated SIEM data and security telemetry, completing up to 80% of requirements from day one.
Continuously monitors live security posture and generates compliance evidence from real events, helping organizations maintain security alongside compliance.
Automates evidence collection, validation, and reporting to reduce manual work and support certifications such as SOC 2 and ISO 27001.
Uses AI to identify potential compliance gaps before they become audit issues, supporting continuous readiness as standards evolve.
Extend compliance visibility, simplify readiness management, and adapt to evolving requirements with capabilities built directly into the Seceon aiSIEM platform.
Track readiness for 20+ global and regional compliance frameworks simultaneously.
Live dashboards showing control coverage, framework progress, and evidence collection.
Easily extend or customize frameworks for industry-specific compliance needs.
Built directly into the Seceon aiSIEM platform.
Seceon aiCompliance CMX360 ensures comprehensive compliance across key global frameworks:
Seceon also supports essential regional standards, ensuring compliance with local regulations:
Measurable returns that transform your security posture and business outcomes
Automated extraction from existing SIEM telemetry eliminates manual evidence gathering.
Real-time dashboards and AI-validated evidence streamline auditor review.
Automation of reporting, evidence mapping, and audit prep cuts down manual labor and consultant expenses.
Immediate leverage of existing security posture provides near-complete framework coverage from day one.
Watch aiCompliance CMX360 automate compliance monitoring, identify control gaps, and turn security evidence into actionable compliance and governance.
Get clear answers about how Seceon aiCompliance CMX360 automates evidence collection, maps security telemetry to compliance frameworks, and keeps organizations audit-ready around the clock.
Seceon aiCompliance CMX360 is a continuous Governance, Risk, and Compliance (GRC) automation module built natively into the Seceon OTM platform. Instead of treating compliance as a separate workstream with periodic manual audits, CMX360 uses the same security telemetry that powers threat detection to automatically map real-time events to compliance controls, generating audit-ready evidence on an ongoing basis rather than at point-in-time checkpoints.
aiCompliance CMX360 supports 45+ global compliance frameworks simultaneously, including NIST CSF, NIST SP 800-53, ISO 27001:2022, SOC 2, PCI-DSS, HIPAA, GDPR, CMMC, FedRAMP, EU DORA, RBI, SEBI CSCRF, and ISO/IEC 42001 for AI governance. Frameworks can be enabled or disabled with a single click, without changing the underlying data collection architecture.
CMX360 auto-completes a large share of framework control requirements directly from accumulated SIEM telemetry, cutting down the manual document chasing that typically consumes weeks of analyst time per audit. Comprehensive, auditor-ready reports that once took roughly two weeks to prepare can now be generated in under one hour.
Yes. CMX360 uses predictive compliance intelligence, powered by Seceon's AI/ML analytics, to flag emerging control gaps before they turn into formal audit findings. Instead of discovering a gap during the audit itself, organizations get advance visibility along with specific, actionable remediation guidance to close it ahead of the audit window.
Yes. For frameworks with mandatory breach reporting windows, such as GDPR's 72 hour rule, CERT-In's 6 hour mandate, India's DPDPA, and Australia's NDB scheme, CMX360 automatically triggers notification workflows and tracks reporting deadlines from the moment an incident is detected, reducing the risk of missing a regulatory deadline during an active incident.
Yes. CMX360 includes a full multi-tenant architecture that lets MSSPs and service providers manage compliance posture across many client organizations from a single console, with per-tenant data isolation. Compliance evidence is also stored with immutable audit trails, including timestamps, source systems, and analyst actions, suitable for regulatory inspections and legal proceedings.
Copyright @Seceon Inc 2026. All Rights Reserved.