Responsive Banner Design
LIVE TELEMETRY ACTIVE
BEHAVIOR SIGNALS SCANNING
THREAT INTELLIGENCE ENRICHING
RESPONSE ENGINE READY
EVENTS  •  TELEMETRY  •  IDENTITY  •  NETWORK  •  ENDPOINT  •  BEHAVIOR  •  THREAT INTELLIGENCE  •  CORRELATION  •  DETECTION  •  TRIAGE  •  RESPONSE  •  REMEDIATION
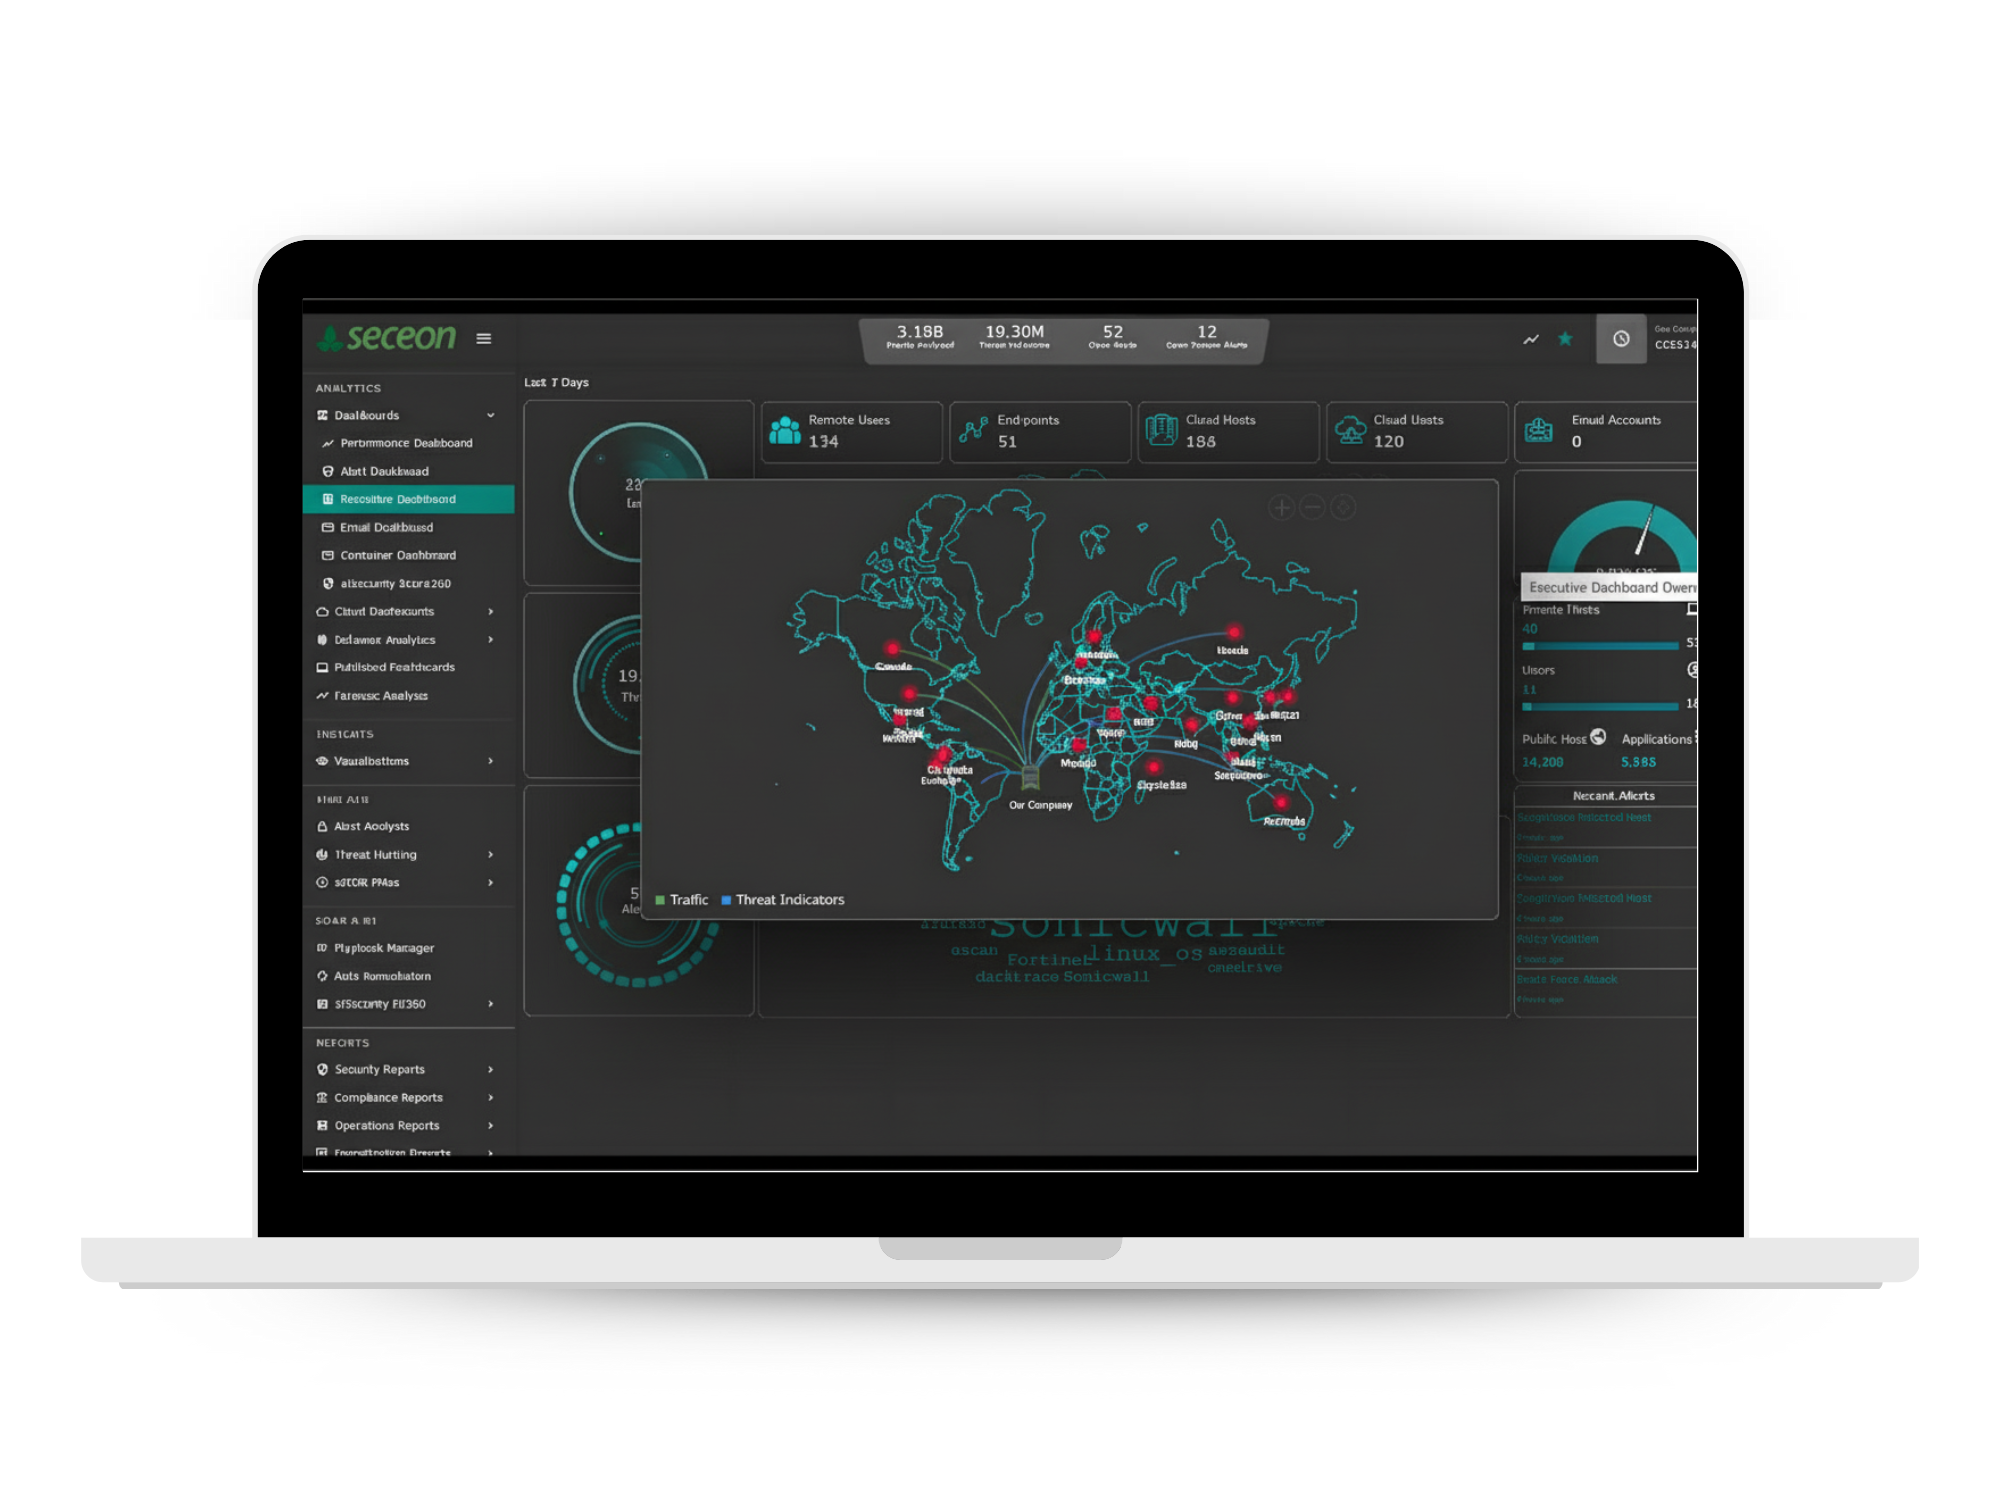
AI-POWERED SECURITY INFORMATION & EVENT MANAGEMENT

Advanced Threat Detection With aiSIEM

Seceon aiSIEM unifies telemetry across logs, identities, networks, endpoints, clouds and applications, applying 360° inference, AI/ML, behavioral analysis and threat intelligence to detect, prioritize and respond to threats in real time. Every event is normalized into one Seceon Event Format (SEF) at ingestion and correlated before it reaches an analyst.

360° Inference

Correlate events, traffic, packets, identities and behavioral patterns.

AI/ML Detection

Use behavioral baselining, profiling and dynamic threat models to identify anomalies.

Threat Intelligence

Enrich detections in-stream with intelligence from 100+ commercial, government, ISAC and dark-web sources.

Automated Response

Accelerate remediation with incident triaging, playbooks and real-time response.

Can your SOC turn every security signal into a prioritized response?

Stop Threats That Legacy SIEMs Can’t Catch

Stop Threats That Legacy SIEMs Can’t Catch

95%

Reduced MTTD

Where traditional SIEMs take days to detect a breach, Seceon aiSIEM detects threats in minutes, cutting MTTD by 95%.

50%

Cut Operational Costs

Seceon aiSIEM automates threat response, cutting SOC costs by up to 50% versus legacy SIEM.

100%

Infrastructure Coverage

Complete visibility across logs, flows, identity, endpoints, cloud and OT through 3,000+ connectors in 13 security domains.

Cybersecurity Challenge & Solution

From Blind Spots to Full Visibility

Gain complete visibility across every asset, user, and flow by AI-driven detection and response.

Security Challenge

Traditional SIEMs Fall Short

Legacy SIEMs are slow, complex, and miss critical threats, leaving blind spots across the network and endpoints.

Teams drown in 500+ daily alerts with 40% false positive rates.

High deployment complexity and slow scaling across hundreds of devices.

Heavy reliance on manual rules and skilled analysts slows response and remediation.

43%
Miss Critical Threats
20%
False Positive Rate

Our Solution

AI-Powered Real-Time Defense

Real-time AI/ML-driven detection with full coverage of NetFlow, logs, servers, endpoints, and cloud assets.

Intelligent filtering, policy tracking and automated alerts remove 93.9% of false alarms in production.

aiSIEM scales to 5M+ events per second and installs in about 5 hours.

Automated threat correlation, behavior-based threat models, and actionable remediation.

99.7%
Detection Rate
93.9%
Fewer False Alarms
How Seceon aiSIEM Works

How Seceon aiSIEM works

From real-time monitoring to automated mitigation, a unified platform for faster, smarter defense.


Real-Time Threat Detection and Response

aiSIEM ingests and analyzes NetFlow and event data the instant it arrives - no storage delays, no indexing wait, ensuring threats are detected as they occur. Logs and flows run through dedicated streaming pipelines and are normalized into one Seceon Event Format (SEF) before analysis.

Real-Time Threat Detection and Response dashboard interface

Automated Threat Mitigation

AI-driven remediation recommendations replace manual analyst work, generating actionable responses automatically. Continuous learning algorithms adapt in real time to evolving threats.

Automated threat mitigation interface showing AI-powered response tools

Comprehensive Visibility

aiSIEM collates events and netflow through 3,000+ connectors across 13 security domains - Linux/Windows servers, Active Directory, firewalls, WAFs, endpoints and cloud platforms - into one unified behavioral analytics portal. Pre- and post-NAT tuples are stitched and X-Forwarded-For headers extracted, so the real client is always visible.

Comprehensive security visibility dashboard with unified network view

Advanced Correlation and Analytics

aiSIEM correlates NetFlow, user, and entity data to build behavioral baselines. Alerts are prioritized by severity and business impact. Multi-stage threat models chain network, identity, endpoint and cloud activity into one incident per attack, so a password-spraying campaign raises one incident, not thousands of alerts.

Advanced correlation and analytics interface with data analysis features

Scalability and Flexibility

aiSIEM is designed to handle large volumes of data and scales to 5M+ events per second. It supports on-premises, cloud, hybrid and air-gapped deployment.

Scalability and flexibility dashboard showing system performance metrics

Event and Contextual Data

Using advanced AI and ML, aiSIEM continuously learns what “normal” looks like in your environment. It detects deviations in real time and reduces false positives. Every event is tagged with its MITRE ATT&CK v20.0 technique.

Event correlation analytics dashboard with log analysis features


How Seceon aiSIEM Works
NetFlow & Network Visibility: Detecting Threats Beyond Logs

aiSIEM provides full-spectrum network visibility by ingesting both NetFlow data and traditional log sources.


netflow-aisiem-diagram
Seceon aiSIEM Benefits

Benefits of Seceon aiSIEM

Fewer alerts to chase, audits that prepare themselves, and a clear view of where your detection coverage stands.

Reduced False Positives

AI-driven analytics and machine learning slash false positives, so analysts work on real risks. At an MSSP partner running 209 customer environments, false alarms fell 93.9% in 15 days and daily triage dropped from 6,447 alerts to 393.
Improved Compliance

PCI DSS, HIPAA, NIST and GDPR compliance evidence is included out of the box, saving weeks of audit preparation.

Enhanced Security Posture

Real-time detection and automated remediation strengthen your defenses, and the MITRE heatmap shows ATT&CK techniques with no detection coverage, so teams close the most valuable gaps first.

ROI-Driven aiSIEM | Seceon Security Platform

What Makes Seceon aiSIEM ROI-Driven?

Measurable returns that transform your security posture and business outcomes


Eliminate Manual Workload

60% Fewer Analyst Hours

Intelligent automation handles routine tasks, freeing your team for strategic initiatives.


End Tool Sprawl

Consolidate 20+ Tools in One

aiSIEM replaces siloed tools - SIEM, SOAR, UEBA, NTA, IDS, and more, cutting costs up to 50%.


Stop 6+ Month Security Gaps

Install in ~5 Hours

Installs in about 5 hours from OVA, AMI or VHD virtual appliances, with full functionality within 2 weeks.


Cost-Efficient Security Monitoring

Asset-Based Pricing

Priced per monitored asset, with no per-GB, per-EPS or per-alert fees, so heavy-traffic networks don't pay more.

Automated Resolution
70%
Of incidents, no analyst needed
Total Savings
50%
Cost Reduction
Security Performance Over Time Illustrative trend
Seceon aiSIEM Cards

Protect Clients Faster with Seceon aiSIEM


MSSP
MSSP Icon

  • Scale to 400+ client assets without increasing SOC count.
  • Cut false alarms 93.9% in production, as measured across 209 MSSP customer environments.
Enterprise
Enterprise Icon

  • Secure 900+ devices in months - instead of 2+ years.
  • Detect advanced threats in under 5 minutes with real-time NetFlow and telemetry analytics.
MSP
MSP Icon

  • Monitor unlimited clients with predictable asset-based pricing, with no per-GB, per-EPS or per-alert fees.
  • Faster Onboarding & Deployment - Onboard new clients in hours with automated playbooks.

Resources - Fortinet Whitepapers

Discover More with Our Resources

Explore our datasheets, case studies and whitepapers to find out how Seceon aiSIEM can streamline your security operations and bolster your cybersecurity defense.

Frequently Asked Questions

Get clear answers about how Seceon aiSIEM uses AI and machine learning to detect threats in real time without manual rule tuning.

What is Seceon aiSIEM and how is it different from a traditional SIEM?

Seceon aiSIEM is an AI native Security Information and Event Management platform that combines machine learning driven threat detection with a unified analytics engine processing over 5 million events per second. Unlike legacy, rule based SIEMs that require analysts to write and continuously maintain correlation rules, aiSIEM deploys Dynamic Threat Models (DTM) that self adjust to an organization's behavior from day one, delivering a 95% reduction in false positives without manual tuning.

What are Dynamic Threat Models and how do they replace manual SIEM rule writing?

Dynamic Threat Models (DTM) are self adjusting AI and machine learning models that adapt to an organization's normal behavior starting from the very first data received, so they are effective from day one without a manual tuning period. aiSIEM includes over 4,000 pre trained models covering all 14 Enterprise tactics and 295 techniques of MITRE ATT&CK v20.0, replacing the ongoing burden of analysts writing and maintaining static correlation rules by hand.

How does aiSIEM achieve a 95% reduction in false positives?

aiSIEM performs multi dimensional correlation across logs, network, identity, cloud, and endpoint data simultaneously, rather than evaluating each source in isolation. Behavioral context enrichment reduces alert noise without losing detection fidelity, and every alert is prioritized using a composite risk score, so analysts see fewer, higher confidence alerts instead of a high volume, low signal alert stream. In production at an MSSP partner running 209 customer environments, false alarms fell 93.9% over 15 days and daily triage dropped from 6,447 alerts to 393.
How much log data can aiSIEM ingest, and how long is it retained?

aiSIEM sustains ingestion of over 5 million events per second, scaling to 2.4 trillion events per day across the full Seceon OTM platform. Logs are retained for up to 7 years in a WORM compliant, tamper proof chain of custody, with OpenSearch backed sub second search across the entire retention window, supported by up to 80% lossless compression at ingestion.

Does aiSIEM include built in cloud security monitoring?

Yes. aiSIEM-CGuard extends aiSIEM's detection intelligence natively into AWS, Azure, Google Cloud and Oracle Cloud Infrastructure through agentless API integration, covering misconfiguration detection via CloudTrail, Azure Defender, and GCP Security Command Center, along with real time cloud threat detection for Lambda abuse, bucket exfiltration, and cross account anomalies, all within the same console and correlation engine as on premises detection.

How fast does aiSIEM detect and help respond to threats?

aiSIEM achieves a mean time to detect (MTTD) of under 5 minutes, compared to an industry average of roughly 197 days to detect a breach. It draws on 100+ threat intelligence sources, including CISA, FBI InfraGard, and Recorded Future, matching indicators in-stream as events arrive and sweeping historical data retrospectively when new indicators appear. It connects natively with aiSOAR 4.0 for automated response actions in under 90 seconds once a threat is confirmed.

Can aiSIEM run alongside Splunk, Microsoft Sentinel or QRadar?

Yes. aiSIEM works next to an existing SIEM without a rip-and-replace. The collector forwards a real-time copy of incoming syslog to the existing SIEM or an archive while processing it, and REST APIs and webhooks sync adjudicated incidents back, so downstream queues receive far fewer alerts.

How does aiSIEM attribute attacks to threat actors?

Multi-tactic alerts are compared with built-in adversary profiles such as Volt Typhoon, Scattered Spider and LockBit to suggest the probable actor. Indicators from CERT-In and NCIIPC are ingested within 5 minutes of publication.

Seceon aiSIEM-CGuard

24/7 Access to Seceon’s Cybersecurity Experts - Because Threats Don’t Wait

Do These Persistent Issues Impact Your Day-to-Day Operations?
  • Large number of failed logins from single/multiple IPs, internal or external, against a single/multiple usernames.
  • Failed logins from new geo locations or a new user device.
  • Large number of account lockouts.
  • High cost of integration, support and maintenance.

    wpChatIcon
    wpChatIcon