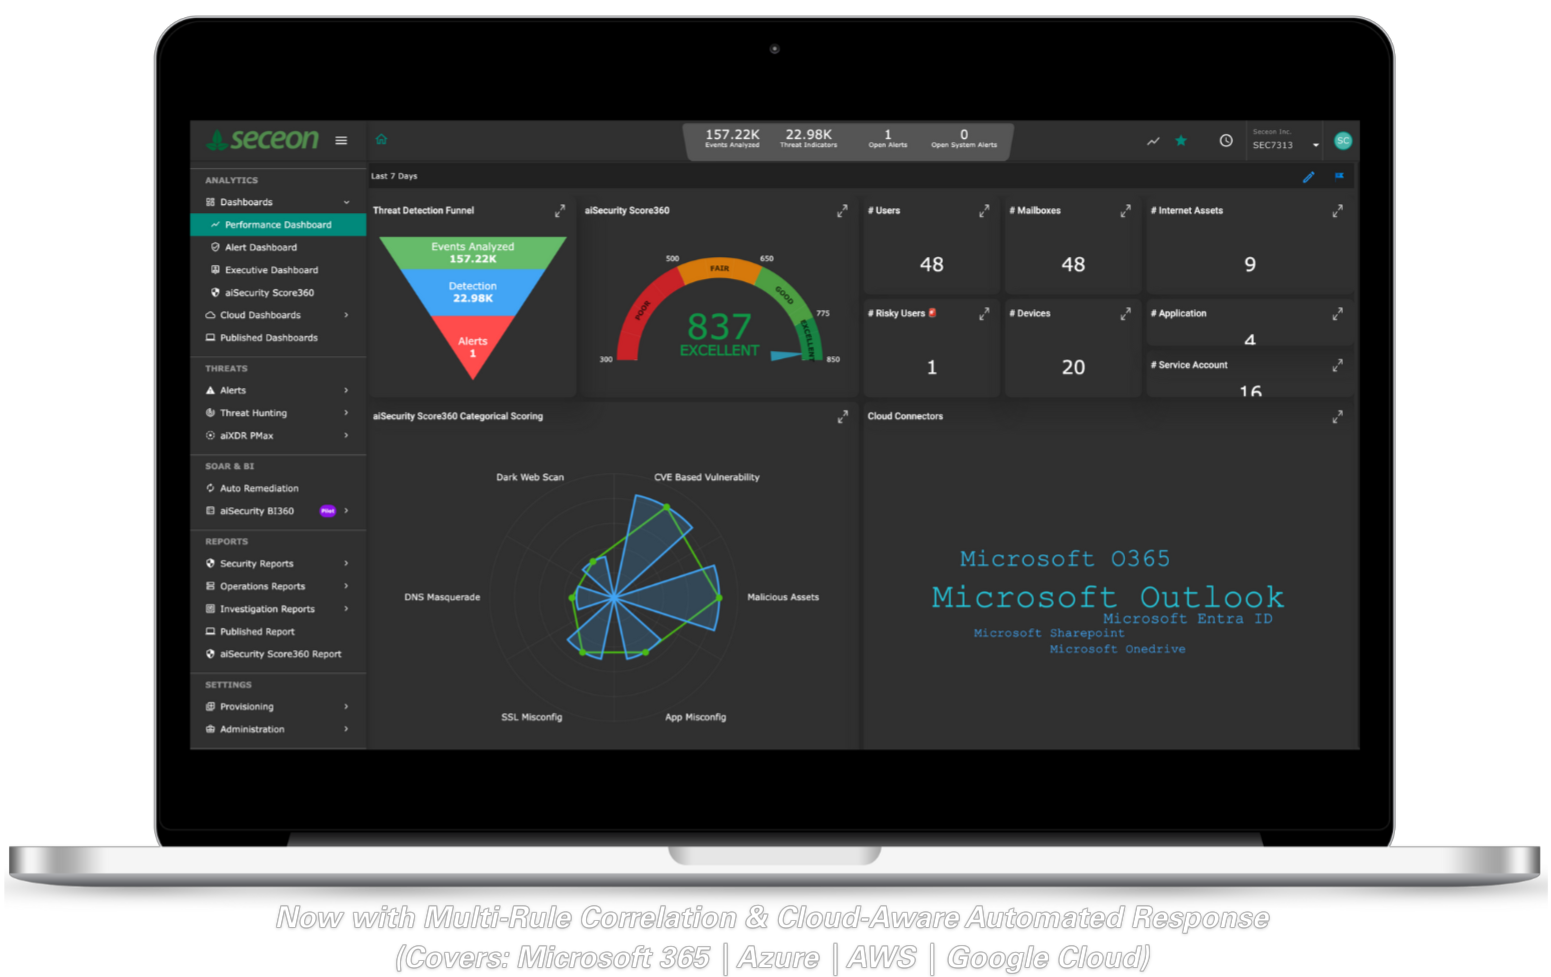
With aiSIEM CGuard 2.0, gain unified visibility, automated response, and complete protection across Microsoft 365, Azure, AWS, and GCP - all in one platform.
AI-driven platform ingests telemetry from your cloud, workloads, and applications, analyzes it in real time, and automatically responds to threats - delivering continuous protection across all environments.
From real-time monitoring to automated mitigation, a unified platform for faster, smarter defense.
Connects alerts, behaviors, and events across Microsoft 365, Azure, AWS, and GCP.
Detects stealthy, low-and-slow attacks that often bypass traditional SIEMs or XDR solutions.
Instantly enforces MFA, revokes OAuth permissions, quarantines identities, and triggers custom playbooks.
Fully adapts to cloud-native APIs and policies, minimizing manual intervention.
Lightweight cloud-native agent collects logs and metrics from hybrid environments without downtime.
Onboards new cloud workloads in minutes - no reinstallation or complex setup required.
aiSIEM CGuard 2.0 delivers quantifiable business value - cutting operational costs, improving detection accuracy, and eliminating pricing uncertainty with a transparent, asset-based model.
Lower SOC Operating Costs
Reduction in False Positives
Faster Threat Detection and Response
Get clear answers about how Seceon aiSIEM-CGuard 2.0 brings cloud security posture management and cloud detection and response natively into a single SIEM, across AWS, Azure, and GCP.
Seceon aiSIEM-CGuard 2.0 delivers Cloud Security Posture Management (CSPM) and Cloud Detection and Response (CDR) as a native capability embedded inside aiSIEM, not as a separate product that needs its own console or integration. All cloud posture findings and cloud threat detections share the same Seceon Event Format (SEF) as on-premises events, which is what enables true unified IT and cloud threat correlation instead of two disconnected views of risk.
aiSIEM-CGuard 2.0 natively integrates with AWS (CloudTrail, Config, Security Hub, GuardDuty, Inspector, IAM Access Analyzer, VPC Flow Logs), Microsoft Azure (Defender for Cloud, Monitor, Policy, Entra ID, Activity Logs, NSG Flow Logs), and Google Cloud Platform (Security Command Center, Cloud Audit Logs, IAM Recommender, VPC Flow Logs) through direct APIs, without requiring a separate CSPM agent.
Yes. On the posture side, it runs automated CIS Benchmark assessments and detects misconfigurations across compute, storage, networking, identity, and data services in AWS, Azure, and GCP. On the detection side, it identifies real-time cloud specific threats such as Lambda abuse, S3 and Blob bucket exfiltration attempts, cross-account role assumption anomalies, and DGA or command-and-control communication originating from cloud workloads.
Cloud posture findings appear inside the aiSIEM correlation engine within 5 minutes or less of scan completion, since aiSIEM-CGuard 2.0 is embedded directly in aiSIEM rather than requiring findings to be exported and re-ingested from a separate CSPM tool.
Yes. Through native integration with aiSOAR 4.0, aiSIEM-CGuard 2.0 can trigger automated cloud response actions, including S3 bucket ACL auto-remediation, security group rule rollback, IAM key rotation, and cloud instance isolation, without requiring a separate remediation workflow outside the platform.
Yes. aiSIEM-CGuard 2.0 maps cloud posture findings to CIS AWS, Azure, and GCP Benchmarks, along with SOC 2, PCI-DSS, HIPAA, GDPR, DPDPA, FedRAMP, and CMMC, giving compliance and cloud security teams a single source of evidence instead of separate cloud and compliance reporting tools.
Copyright @Seceon Inc 2026. All Rights Reserved.