Add Endpoint Protection, Detection, and Response - EDR, EPP, DLP, FIM, and automated remediation to strengthen your cybersecurity posture.
Request demo
Empower your organization with comprehensive Endpoint Protection, Detection, and Response - including EDR, EPP, DLP, FIM, and automated remediation for total endpoint defense. Seceon aiXDR-PMax delivers continuous monitoring, intelligent threat detection, and proactive response to safeguard devices across your entire digital ecosystem.
Your endpoint resilience starts here.
Unified visibility and automated response across endpoints, networks, and cloud assets.
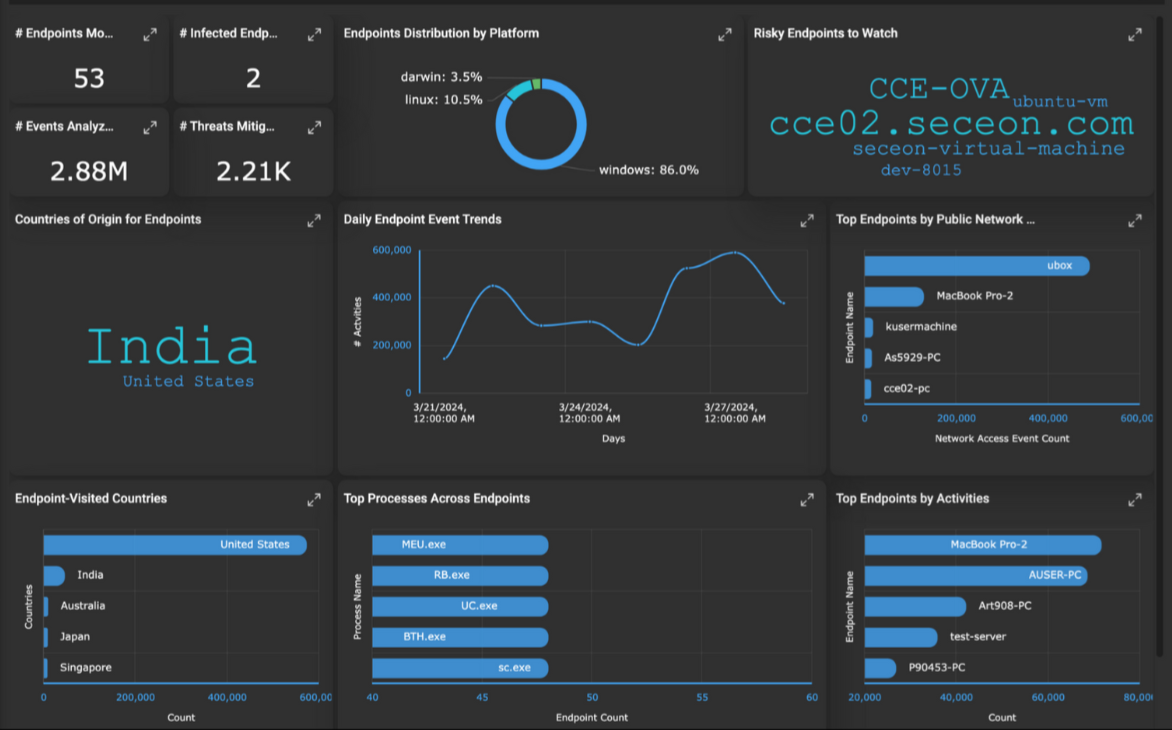
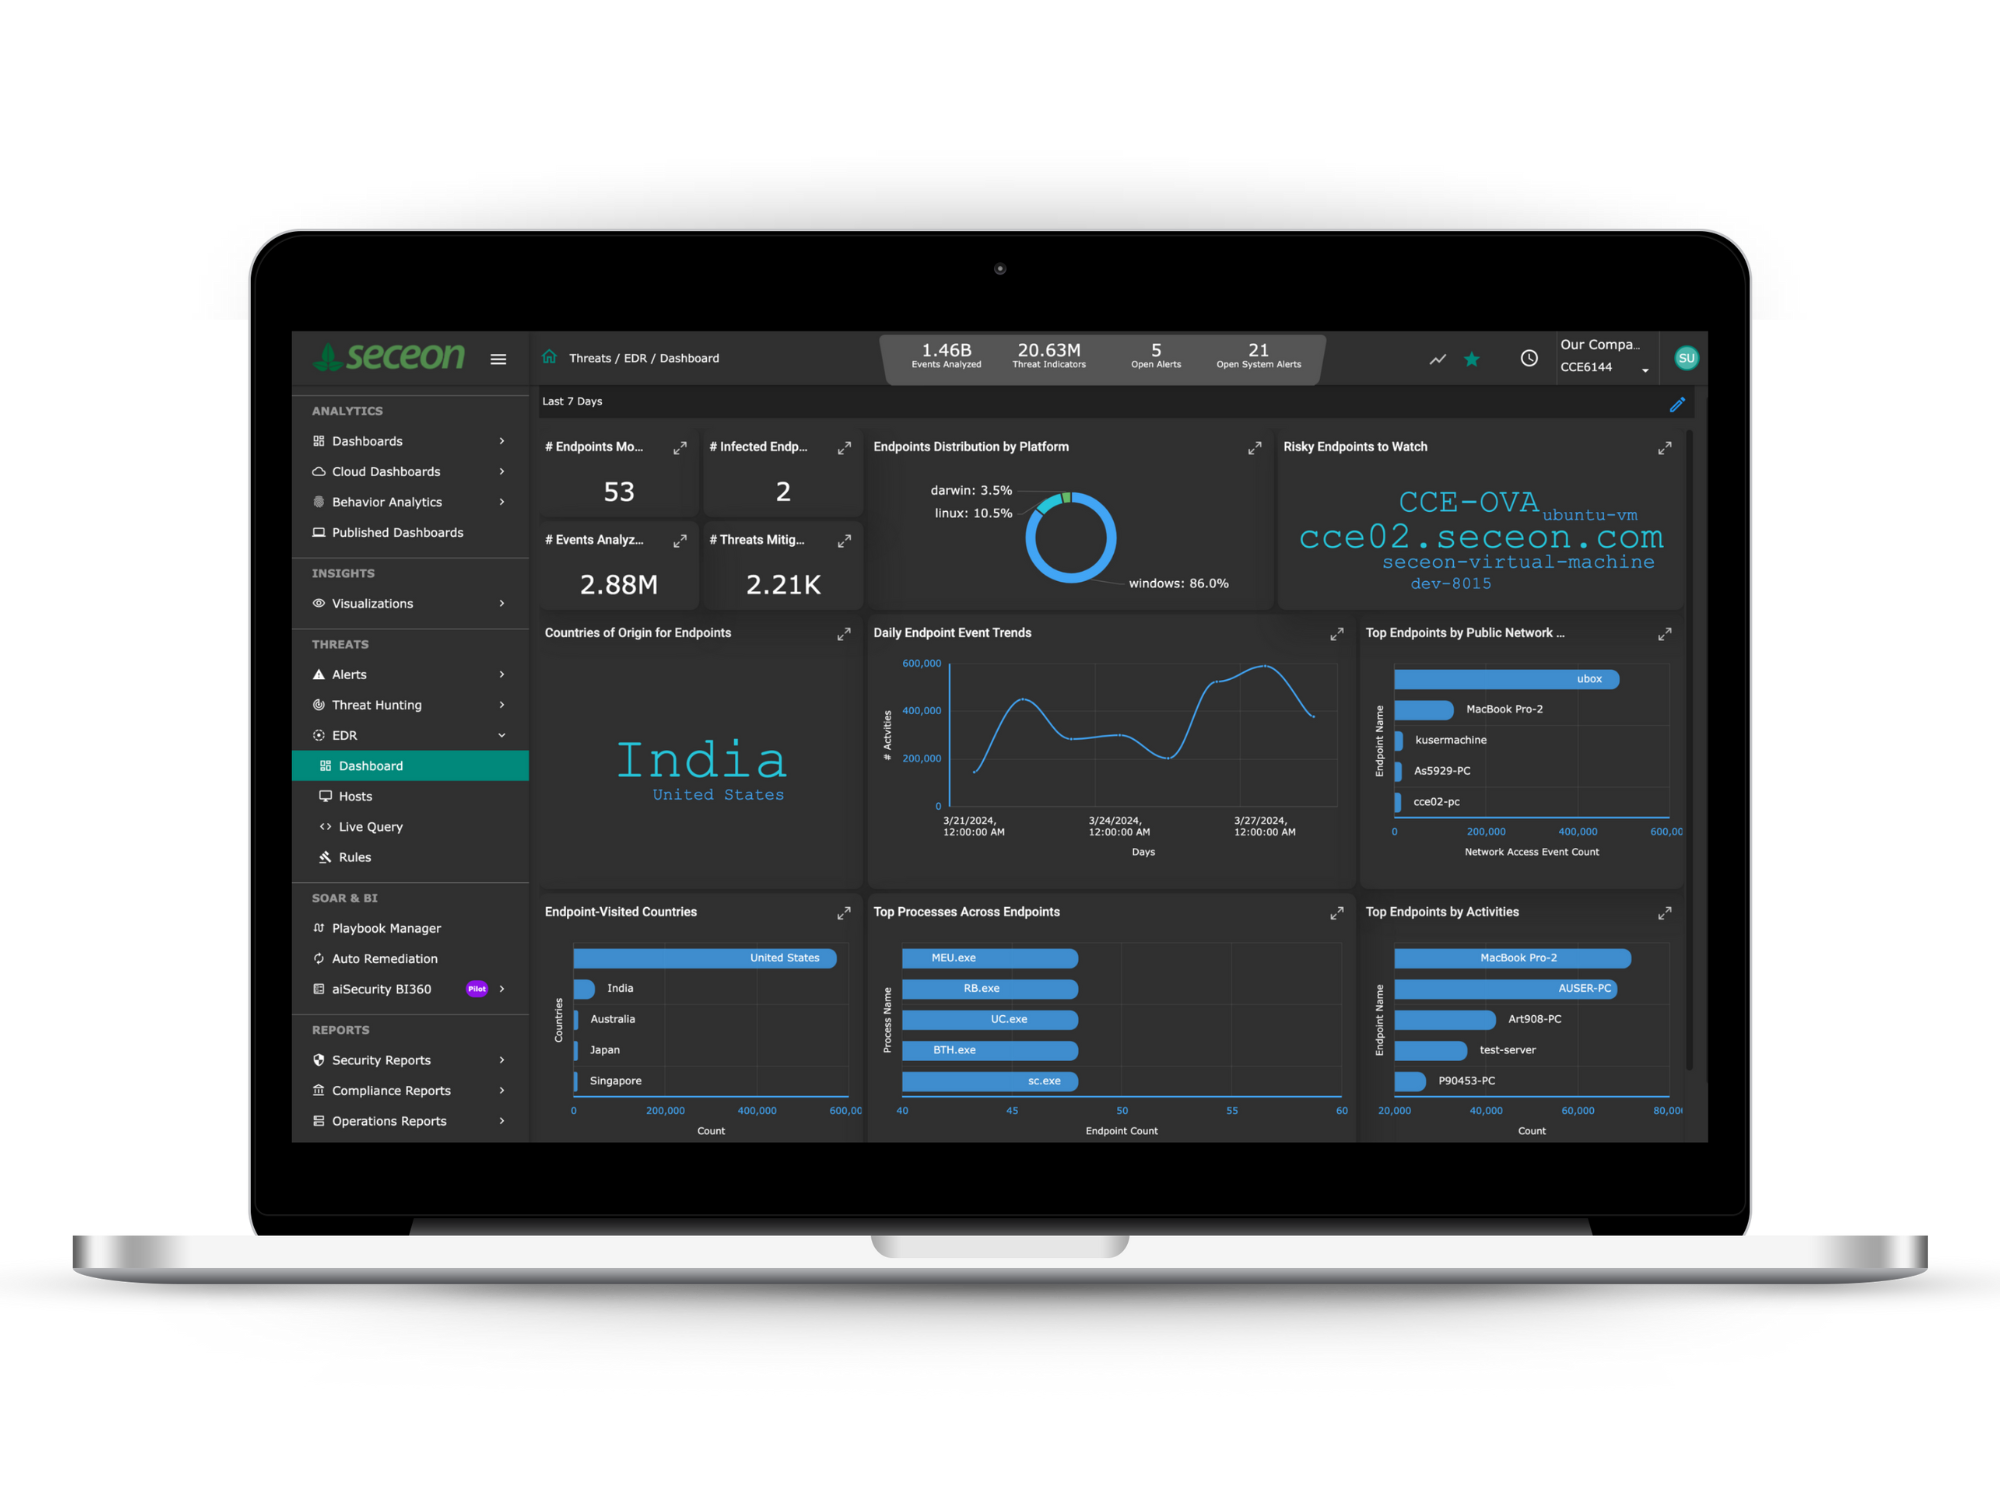
See Endpoints Monitored, OS Distribution, and Infected Endpoints in real time. Identify risky devices directly from the dashboard to maintain full endpoint health.
View Top Endpoints by Activity and Public Network Access, track Countries Visited, and spot Risky Endpoints to uncover unusual patterns.
Analyze Top Processes Running, Query Result Distributions, and Network Stats using AI/ML baselining. Detect anomalies and trigger alerts as soon as abnormal behaviors appear.
Interactive charts show Endpoint Activities Trend, Process Analytics, and Network Events for end-to-end visibility and proactive threat hunting.
Unlike conventional cybersecurity tools that react after an attack, aiXDR-PMax continuously monitors and responds in real time, preventing threats before they escalate
Combining EDR, EPP, UEBA, and threat intelligence, aiXDR-PMax identifies phishing, malware, insider threats, and multi-layered attacks across your entire environment.
The platform collects telemetry from endpoints, servers, cloud, and IoT/OT systems, correlates events with context, and presents transparent alerts, giving analysts a complete picture of attacks.
Teams can integrate aiXDR-PMax with their existing EDR/EPP stack or deploy the full solution with built-in endpoint protection, enabling high-fidelity detections.
By continuously monitoring endpoints, networks, and cloud systems, aiXDR-PMax detects anomalies, compromised credentials, and ransomware early, stopping threats.
Integrate aiXDR-PMax with your existing EDR and EPP solutions to centralize threat detection and automated response.
Protect workloads across AWS, Microsoft Azure, and Google Cloud with real-time monitoring and AI-driven threat detection.
Extend aiXDR-PMax with your SIEM, SOAR, and UEBA systems to correlate events, automate responses, and detect anomalies.
Measurable returns that transform your security posture and business outcomes
AI-driven correlation and behavioral analytics identify and contain threats before they spread.
Precision-based detections and noise suppression eliminate false positives and analyst burnout.
Real-time visibility and automated response shrink detection windows and stop lateral movement early.

Get clear answers about how Seceon aiXDR-PMax unifies endpoint detection, data loss prevention, and file integrity monitoring into a single lightweight agent.
Seceon aiXDR-PMax is an Extended Detection and Response module that unifies endpoint detection, data loss prevention (DLP), and file integrity monitoring (FIM) across IT, OT, cloud, network, and identity domains, all from a single lightweight agent and one management console. Unlike XDR platforms built by stitching together acquired products, aiXDR-PMax is built natively on the Seceon Event Format (SEF), so endpoint, DLP, and FIM data correlate with zero API latency instead of passing through separate integrations.
The aiXDR-PMax agent has an installed footprint of under 50MB and uses less than 1% CPU while idle, so it can run on resource constrained endpoints without a noticeable performance impact. It supports Windows 10, 11, and Server 2008 and later, macOS 12 and later, and Linux kernel 4.19 and later, including major distributions such as RHEL, Ubuntu, SUSE, and Amazon Linux.
Yes. aiXDR-PMax uses behavioral detection from day one, without relying on signatures for unknown threats, combined with memory forensics and process chain analysis to catch process injection, code hollowing, credential dumping, and other fileless malware techniques. It provides at least 95% endpoint technique coverage across the MITRE ATT&CK Enterprise matrix.
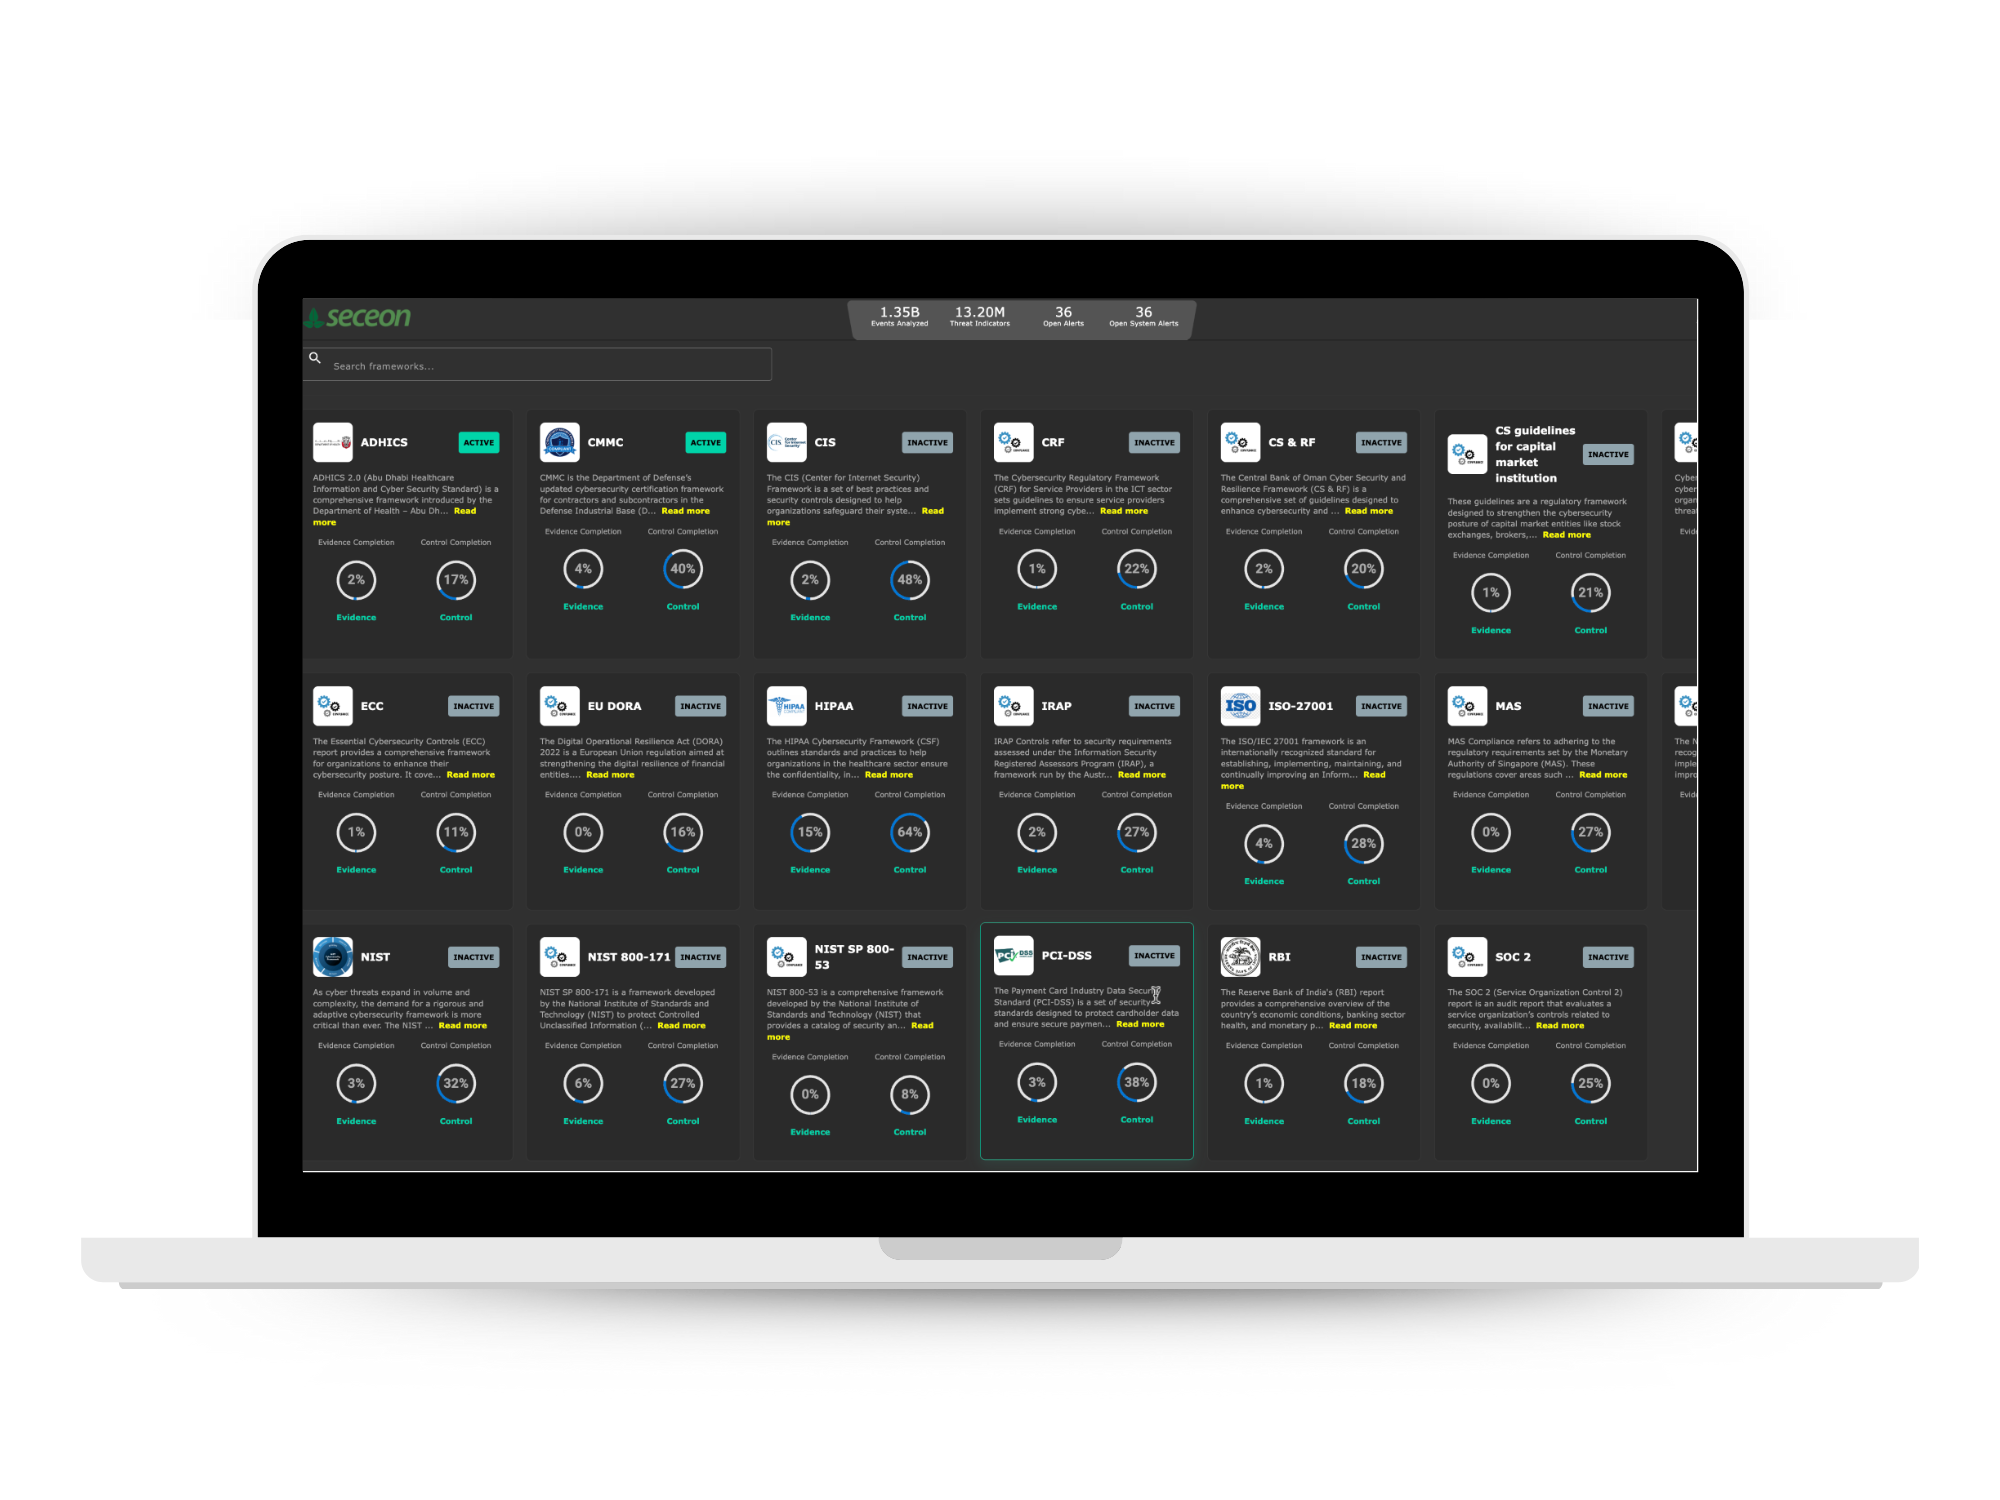
Yes. Built-in DLP monitors sensitive data movement across endpoints and detects data exfiltration for categories such as PII, PHI, PCI cardholder data, credentials, and classified documents, using UEBA behavioral baselines for added context. Built-in FIM monitors file creation, modification, and deletion in real time across Windows, Linux, and macOS, providing evidence for compliance frameworks such as PCI-DSS, HIPAA, SOX, NIST, and CERT-In.
Yes. For organizations with existing endpoint security investments, aiXDR-PMax supports integration with third party EDR tools including CrowdStrike Falcon, SentinelOne, Carbon Black, and Microsoft Defender, so those telemetry sources feed into the same correlation and response pipeline rather than requiring a rip and replace approach.
aiXDR-PMax automates roughly 70% of incident response through integrated SOAR playbook execution, achieving a mean time to respond of under 90 seconds. Automated actions include endpoint isolation, process termination, evidence collection, and full attack chain reconstruction from initial access through impact, without waiting for manual analyst triage.
Copyright @Seceon Inc 2026. All Rights Reserved.