Responsive Banner Design

What is Malware Detection?

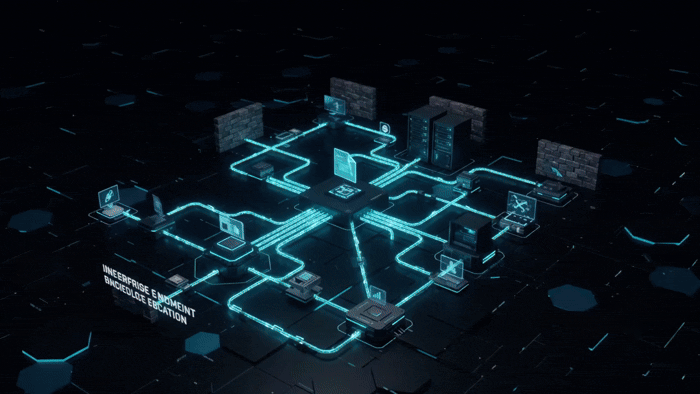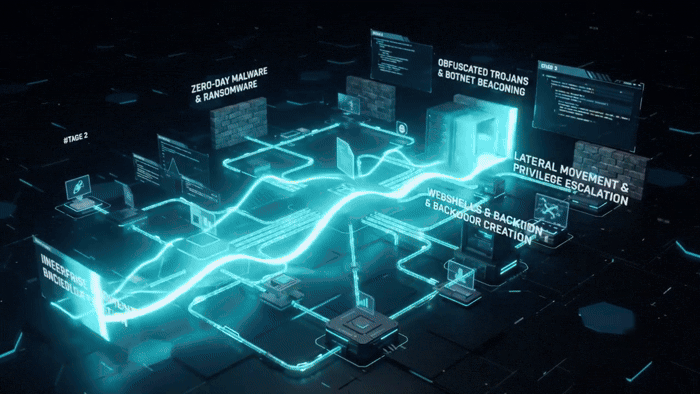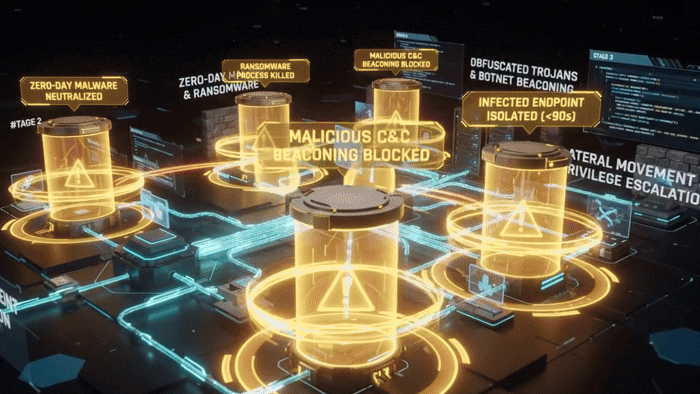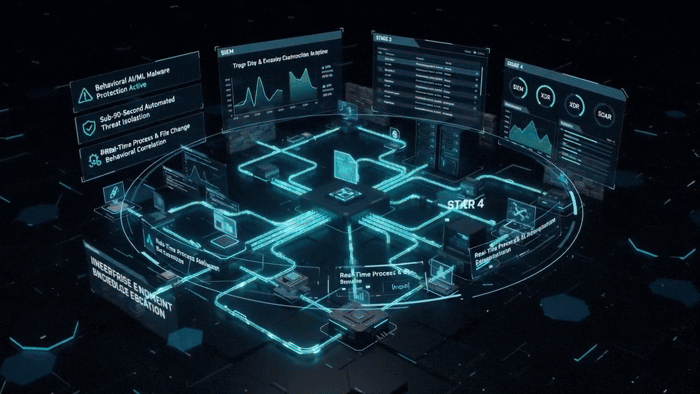
Malware is one of the most common causes of endpoint compromise. Various types of malware such as Trojans, Worms, and Botnets are used by cybercriminals to infect devices and launch attacks.

Malware activities include:

  • Reconnaissance on internal systems
  • Establishing backdoors and deploying webshells
  • Lateral movement within networks
  • Privilege escalation to gain higher control
  • Beaconing with external C&C centers

More alarmingly, Zero-Day Malware and Ransomware have the potential to cause massive financial and operational damage, and their unpredictable nature makes them particularly worrisome for industries globally.

Challenges

Vulnerable Endpoint Exposure

Endpoints outside organizational firewall are often unguarded against malicious websites or torrent-based activities that invite malware.

Evasive Malware Tactics

Evasive techniques, including obfuscation, encryption, and stealth mode, make malware detection significantly more challenging.

Evolving Attack Vendors

Evolution of known vectors over time renders futility to previous tried defenses, signatures and heuristic-based detection techniques.

Seceon aiXDR-PMax

Catch malware by what it does, not what it looks like

Behavioral detection across endpoints, memory and the network finds unknown and fileless malware, then contains it automatically.

Behavioral EDR

No signature needed for unknown threats

Behavioral detection from day one, with process chain analysis that follows every step a threat takes.

Illustrative example.

≥95%MITRE ATT&CK endpoint technique coverage
3OS platforms: Windows, macOS, Linux

Memory analysis

Fileless malware

Memory forensics catches threats that never touch the disk.

Process injectionCode hollowingCredential dumping

Ransomware

Pre-encryption detection

Flags mass file-encryption behavior before the payload spreads.

Potential Ransomware in Progress alert

Built-in alerts

Malware detections, ready to use

Threat intelligence

Known malware and C2

2B+

IOCs from 100+ sources, plus DGA prediction for malware such as WannaCry, Conficker and Ramnit

Automated response

<90s

Contain the endpoint

70% automated response rate through native SOAR.

Investigation

From initial access to impact

Full attack chain reconstruction, with built-in file integrity monitoring that records file creation, modification and deletion.

Works with what you have

Already running an EDR?

aiXDR-PMax integrates with existing EDR tools, so their telemetry correlates with network, identity and cloud data.

CrowdStrike FalconSentinelOneCarbon BlackMicrosoft Defender
<50MB

Lightweight agent

Protection without the slowdown

Under 1% idle CPU on Windows, macOS and Linux, deployable through AWS SSM, Azure VM Extension, GCP OS Config or Kubernetes.

Malware Detection FAQs

Explore how AI-powered malware detection helps identify evolving threats, detect suspicious behavior, and support faster incident response with Seceon.

How can businesses detect malware that traditional antivirus software misses?

Traditional antivirus software often relies on known malware signatures, which can make unfamiliar or modified threats harder to detect. Businesses can strengthen detection by monitoring suspicious processes, file changes, user activity, and network connections alongside threat intelligence.

Seceon uses AI/ML-driven behavioral analysis through its aiSIEM and aiXDR solutions to help identify suspicious activity associated with unknown malware and evolving threats. Detection depends on the telemetry available and deployment configuration.

What should businesses look for in an AI-powered malware detection solution?

Businesses should evaluate malware detection solutions based on behavioral analytics, threat intelligence, endpoint and network visibility, incident investigation, response automation, integration support, and scalability. The ability to correlate related events is particularly important when malware activity spans multiple systems.

Seceon's OTM (Open Threat Management) Platform brings together aiSIEM and aiXDR to correlate security events, analyze behavioral patterns, and support threat detection and response. Businesses should assess product capabilities and integrations against their specific security requirements.

How can organizations detect zero-day malware before it causes serious damage?

Zero-day malware may evade defenses that depend on previously known signatures. Organizations can improve detection by monitoring behavioral anomalies, suspicious process execution, unexpected file changes, and unusual network connections instead of relying exclusively on known malware indicators.

Seceon uses AI/ML-based behavioral analysis and Dynamic Threat Models through its aiSIEM and aiXDR solutions to help identify zero-day threats and advanced evasive activity. No security solution can guarantee detection of every zero-day attack before damage occurs.

How can security teams detect ransomware before it spreads across a network?

Security teams should monitor unusual file modifications, suspicious process activity, abnormal network connections, and lateral movement between systems. When ransomware activity is detected, isolating affected endpoints and stopping malicious processes can help limit its spread.

Seceon combines aiSIEM event correlation with aiXDR endpoint detection and response capabilities. Depending on the deployed integrations and configuration, response actions can include endpoint isolation, stopping malicious processes, and quarantining malicious files.

How does AI-based malware detection identify fileless malware and evasive attacks?

Fileless malware can operate through system memory, scripts, or legitimate administrative tools, making file-signature scanning alone insufficient. Detecting these threats requires analyzing process execution, process relationships, scripts, and network activity for suspicious behavior.

Seceon aiXDR supports behavioral detection and endpoint telemetry analysis to help identify suspicious process activity and evasive techniques. Combined with aiSIEM, these capabilities help security teams correlate endpoint signals with other events to investigate potential threats. Detection coverage depends on the telemetry and features enabled in the deployment.

Can malware detection software automatically contain threats, or is manual intervention required?

Malware detection software can automate selected response actions when configured rules or response policies identify a qualifying threat. Actions may include isolating an affected endpoint, stopping a malicious process, or quarantining a malicious file. Complex incidents may still require investigation and analyst approval.

Seceon aiXDR supports endpoint containment and remediation, while aiSIEM helps correlate events and investigate threats. Security teams can determine the appropriate level of automation based on their risk tolerance, integrations, and response policies.

Summary Section

Summary

Seceon’s AI-driven solution detects and prevents malware by analyzing system behavior, identifying malicious activity in real-time, and automatically blocking threats to ensure strong protection against malware infections and system compromise.

Seceon aiSIEM-CGuard

24/7 Access to Seceon’s Cybersecurity Experts - Because Threats Don’t Wait

Do These Persistent Issues Impact Your Day-to-Day Operations?
  • Large number of failed logins from single/multiple IPs, internal or external, against a single/multiple usernames.
  • Failed logins from new geo locations or a new user device.
  • Large number of account lockouts.
  • High cost of integration, support and maintenance.